

ZachXBT says undercover probe exposed Chinese syndicate laundering $1B for Lazarus Group
On-chain sleuth ZachXBT disclosed that he posed as a client and fronted nearly $350,000 to infiltrate a Chinese laundering syndicate tied to North Korea's Lazarus Group, uncovering intelligence that helped freeze funds stolen in the $1.5 billion Bybit hack.
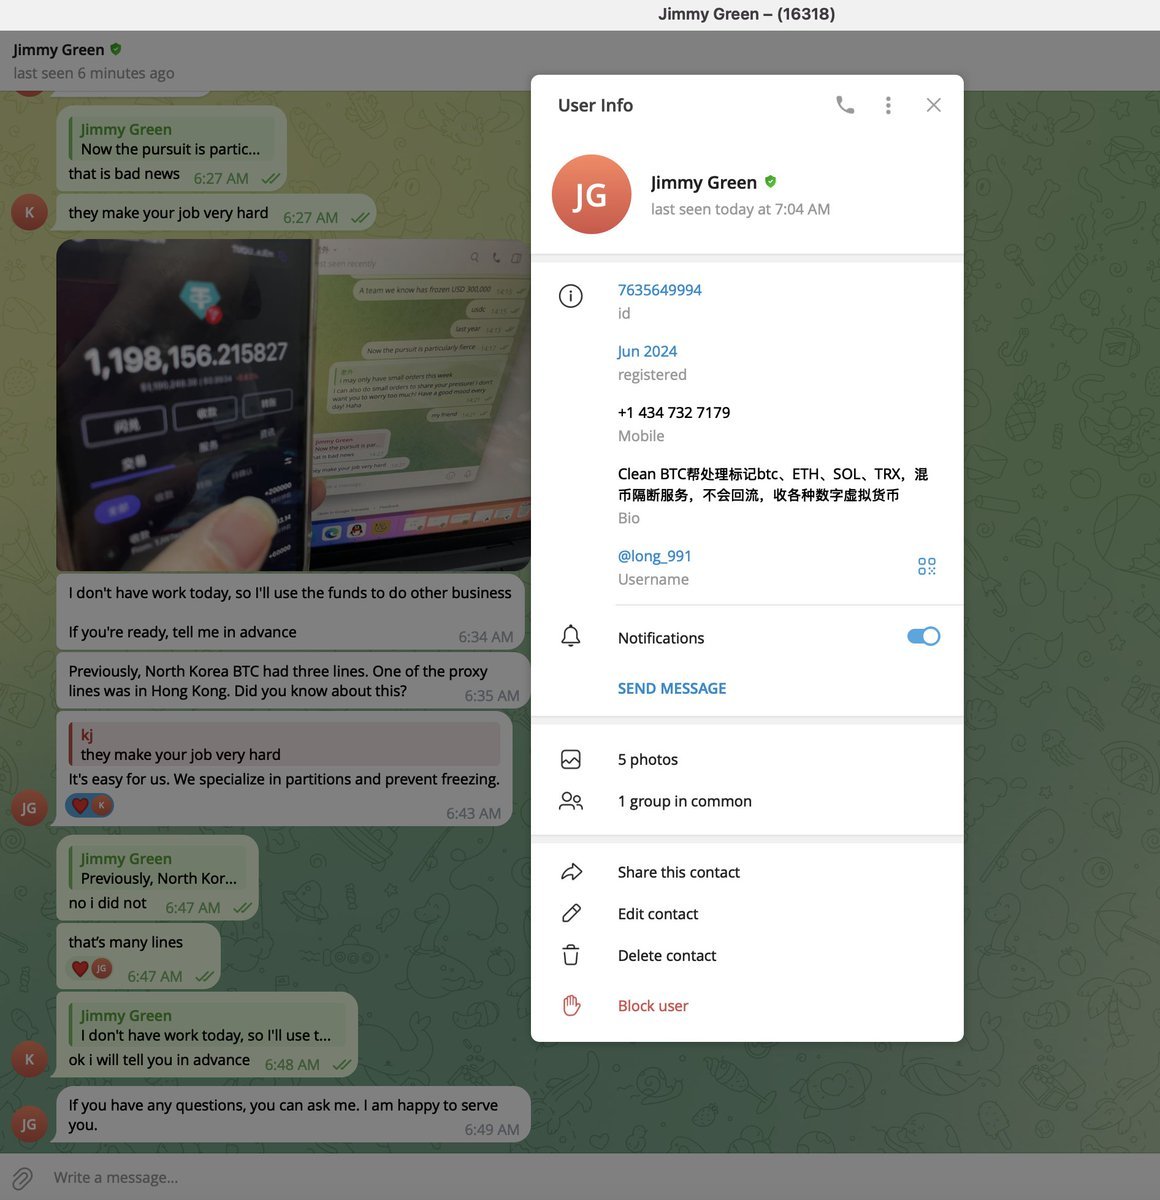
Blockchain investigator ZachXBT disclosed on Oct. 5 that he posed as an undercover client to infiltrate a Chinese organized crime syndicate that he alleges laundered more than $1 billion across multiple exploits for North Korea's Lazarus Group. According to his account, ZachXBT fronted 349,700 USDC in stablecoin trades to cultivate a relationship with a counterparty using the Telegram alias Jimmy Green.[1][4][5]
The undercover effort began after the February 2025 theft of roughly $1.5 billion from Bybit, an attack attributed by the FBI to North Korean actors. ZachXBT noticed Telegram and Discord accounts soliciting laundering services for stolen assets and initiated repeated swaps, sending USDC on Ethereum in exchange for USDT on Tron while absorbing a 5% loss per order. Over time, the contact revealed details about laundering pipelines in mainland China and Hong Kong, shared bridge transactions, and foreshadowed fund transfers to Solana before they occurred.[1][4][5]
The intelligence helped ZachXBT identify a cluster of more than $12 million in Bybit exploit funds dispersed across Bitcoin, Ethereum, Solana, and Tron, which led to Tether freezing 442,000 USDT. ZachXBT also linked the operation to transactions connected to the Poloniex hack and sanctioned marketplace conglomerate Huione Guarantee, stating that he is seeking donations and grants to continue pursuing sensitive, high-risk investigations.[1][3][5]
Key facts
- ZachXBT reported that he posed as a client to infiltrate a Chinese crime syndicate he alleges laundered over $1 billion across exploits for North Korea's Lazarus Group.
- ZachXBT fronted 349,700 USDC to trade with a Telegram contact known as Jimmy Green, absorbing a 5% loss on each order to build trust.
- The operation traced more than $12 million in stolen Bybit funds moving across Bitcoin, Ethereum, Solana, and Tron.
- Tether subsequently froze 442,000 USDT connected to the identified laundering cluster.
- ZachXBT matched communications from the contact to prior freezes tied to the Poloniex exploit and funds laundered for Huione Guarantee.
- The $1 billion laundering estimate and Jimmy Green links are findings reported by ZachXBT and remain separate from official government attributions.
Sources · 5 sources
- CR
CryptoSlateArticle ·
ZachXBT infiltrates $1B crypto syndicate to expose Lazarus Group Blockchain investigator ZachXBT said he infiltrated a Chinese laundering syndicate by posing as a cryptocurrency client and funding repeated stablecoin trades. In an Oct. 5 disclosure , he alleges the network laundered more than $1 billion across exploits for Lazarus Group. He said he fronted 349,700 USDC to build a relationship with a contact using the alias Jimmy Green. According to his account, the repeated exchanges led to private conversations about moving funds stolen from Bybit in 2025. He reported tracing a cluster involving more than $12 million in Bybit funds and a later 442,000 USDT freeze by Tether . Becoming a client ZachXBT said the investigation began after the February 2025 Bybit exploit, when he noticed at least 15 accounts asking for help with orders he linked to stolen funds in public Telegram and Discord groups. He contacted several of those accounts. One was Jimmy Green, the Telegram alias of the person with whom he subsequently exchanged funds. On March 6, 2025, ZachXBT said he funded a new Ethereum address with 349,700 USDC in preparation for transactions with the contact. The arrangement involved sending his USDC on Ethereum in exchange for the contact's USDT on Tron. He then completed additional transactions to build trust. As he built trust through repeat exchanges, ZachXBT said the contact began discussing movements of Bybit funds for North Korea before they occurred. The conversations also included details about operations in Hong Kong and mainland China. In one example, he said the contact told him funds would move to Solana, and the movement happened the following day. On March 12, 2025, ZachXBT said the contact sent a screenshot of a cross-blockchain transfer. He matched its amounts and timing to an order on the THORChain transaction explorer created within minutes of the message. According to ZachXBT, the contact also supplied three Solana addresses. He said these exposed a cluster involving more than $12 million in Bybit exploit funds moving through Bitcoin, Ethereum, Solana and Tron. He separately reported that Tether later froze 442,000 USDT linked to the cluster. That is the specific freeze amount described in this part of his investigation; the larger cluster figure represents funds he said he traced. Related Reading Did Tether just freeze $72M in USDT with no link to a hack in Monero money laundering sting? The account also reaches beyond Bybit. ZachXBT said the contact mentioned a team whose funds had been frozen in 2024. He said that matched an on-chain freeze of 332,000 USDC tied to the Poloniex exploit. The Bybit backdrop and the cost of access In a Feb. 26, 2025 alert , the FBI said North Korea stole approximately $1.5 billion in virtual assets from Bybit on or about Feb. 21. It called the specific malicious activity TraderTraitor. At the time, the FBI said some stolen assets had been converted into Bitcoin and other virtual assets dispersed across thousands of addresses on multiple blockchains. It urged private-sector services to block transactions connected to the laundering addresses. The syndicate's total and the links to Jimmy Green remain ZachXBT's findings, separate from the FBI's attribution of the theft. Allegations involving a Chinese over-the-counter trader surfaced in October 2024. The latest account describes how ZachXBT obtained information by becoming a trading counterparty himself. ZachXBT said he fronted 349,700 USDC for the case and lost 5% on each order. The amount advanced is distinct from his net loss, which he did not quantify in the disclosed figures. He appealed for continued foundation grants and individual donations to support higher-risk investigations. He said intelligence from these trades helped freeze funds tied to the Bybit exploit. The post ZachXBT infiltrates $1B crypto syndicate to expose Lazarus Group appeared first on CryptoSlate .
Open source - CR
CryptoSlate@CryptoSlatePost on X ·
ZachXBT says he traced over $12M in Bybit exploit funds after posing as a client of an alleged laundering network. He reports Tether later froze 442,000 USDT. His $1B+ Lazarus laundering claim remains his finding, separate from the FBI's attribution. https://t.co/kxjFRbJ80Q
Open source - CB
Coin Bureau@coinbureauPost on X ·
JUST IN: ZachXBT asks for donations after spending $349.7K of his own money to investigate $1B+ crypto exploits. The request came after he revealed the full story behind one of his riskiest investigations yet. He says he used the money to pose as a laundering client inside a Chinese syndicate moving funds for DPRK. The trail led to “Jimmy Green,” a Telegram user allegedly helping move funds from the $1.5B Bybit hack. To keep Jimmy talking, ZachXBT says he had to accept a 5% loss on every order. Over time, Jimmy appeared to trust him, sharing wallet addresses, screenshots and bridge transactions in real time. ZachXBT says he matched those flows on-chain, and evidence eventually helped Tether freeze $442K USDT. He says he is now seeking grants and donations to keep taking on high-risk investigations like this. He also revealed he is currently sitting on “significant findings” from other cases.
Open source - ZA
ZachXBT@zachxbtPost on X ·
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group. Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain. https://t.co/jauRRt8875
Open source - PR
ProtosArticle ·
ZachXBT poses as money launderer to infiltrate Lazarus network Crypto sleuth ZachXBT claims he was able to infiltrate a Chinese organized crime syndicate that’s laundered over $1 billion in crypto for North Korean hacker collective Lazarus Group. Last week, Zach uncovered multiple Chinese Telegram and Discord accounts looking for help with laundering funds stemming from September’s $387 million Bitget hack. According to Zach, he was able to contact one of these accounts, named “Jimmy Green,” and pose as a money laundering client to gather intel. As part of this process, he sent them various sums of money to be laundered and noted down crypto addresses and other key information. 1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group. Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain. pic.twitter.com/jauRRt8875 — ZachXBT (@zachxbt) October 5, 2026 Read more: The solution to crypto’s Lazarus problem could be simpler than expected He revealed that he fronted almost $350,000 to do this, and that every order with Jimmy Green lost him 5%. There was “no guarantee Jimmy wouldn’t disappear with the funds” Zach claimed, adding that there was “an unknown amount of personal risk from dealing with the syndicate.” His intel was later used to freeze funds linked to 2025’s $1.5 billion Bybit hack, and help connect crypto transactions to illicit activity. Jimmy claimed his team laundered most Bybit funds Jimmy told Zach that his team was responsible for laundering most of Bybit’s stolen funds, and shared various exploiter addresses and an example of bridging funds using THORSwap. When Jimmy revealed he laundered $3 million for another client, Zach was able to link the funds to Huione Guarantee, a sanctioned conglomerate that ran a multi-billion-dollar criminal marketplace. Zach also linked a 2024 $100,000 freeze, targeting Jimmy’s transactions, to the $100 million hack of Poloniex. Lazarus Group launderer eats wild game and goes to Disney Jimmy also told Zach that they like to eat wild rabbit and birds, sending him pictures of the cooked dish. Other small talk covered Jimmy’s interest in fat-reducing foods and “American coffee,” and they also shared their love for Chinese mahjong and vacations to Disney. 11/ Throughout our conversations, Jimmy and I had a lot of small talk in between discussing laundering for DPRK. He talked about playing mahjong, hunting wild rabbits, food, his fat reducing meal, family life, and vacations at Disney. (His awkward grammar can be explained by… pic.twitter.com/84HwgBYB9I — ZachXBT (@zachxbt) October 5, 2026 Read more: Crypto sleuth links $500M in Iranian USDT to stolen Bybit funds Zach says he hopes he’ll “continue receiving grants from foundations and donations from individuals, as it enables me to take on higher risk for unique cases that others may not consider viable.” He noted that these investigations can’t be shared sooner due to sensitive investigations with private investigators and law enforcement. As such, he says he’s “sitting on significant findings from other cases.” Got a tip? Send us an email securely via Protos Leaks . For more informed news and investigations, follow us on X , Bluesky , and Google News , or subscribe to our YouTube channel. The post ZachXBT poses as money launderer to infiltrate Lazarus network appeared first on Protos .
Open source