

Researchers propose Shielded Bitcoin design for private transfers without soft fork
Researchers at [alloc] init have published a proposal for Shielded Bitcoin, a metaprotocol that adapts Zcash-style encrypted notes and zero-knowledge proofs to allow private bitcoin transfers without altering Bitcoin's consensus rules.
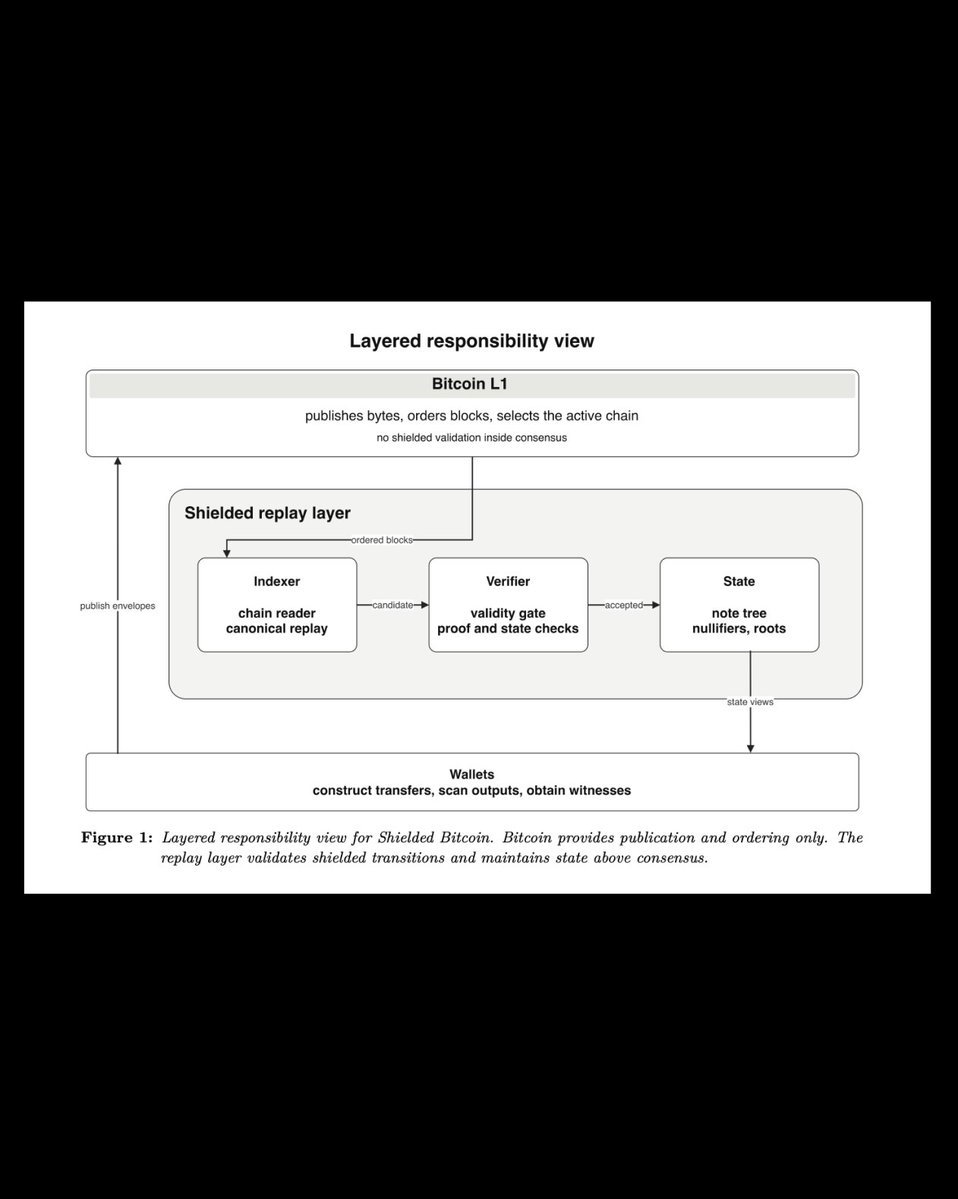
Researchers Clara Shikhelman, Mikhail Komarov, and Aleksei Moskvin of [alloc] init published a paper proposing Shielded Bitcoin, a metaprotocol designed to enable private BTC transfers directly on Bitcoin's base layer without requiring a soft fork or changes to network consensus rules. The architecture borrows Zcash's encrypted-note and nullifier model alongside zero-knowledge proofs to conceal transaction amounts, senders, and recipients.[1][2][5][7][10]
Under the proposed framework, Bitcoin miners and nodes would not validate the shielded transaction state directly. Instead, Bitcoin serves as an ordering and publication layer—with the initial profile utilizing OP_RETURN—while participating implementations scan blocks to construct note trees and spent-note sets. The design includes view-only keys that enable selective disclosure for compliance or audits, although certain metadata like transaction fees, timing, and input and output counts remain visible.[9][10]
Shielded Bitcoin is currently a research paper rather than a live product. According to Komarov, the system relies on an experimental technique called witness encryption under a design dubbed Bitcoin PIPEs, with shielded transactions estimated at roughly 700 vbytes—about four times the size of typical Bitcoin transactions. The specification also leaves peg-in and peg-out mechanisms outside its scope, while other researchers have raised questions regarding quantum resistance and anonymity. Following the proposal, Bitwise Europe Head of Research André Dragosch characterized the concept as a potential headwind for dedicated privacy coins.[3][4][6][8][10]
Key facts
- Researchers Clara Shikhelman, Mikhail Komarov, and Aleksei Moskvin at [alloc] init authored a Sept. 24 paper proposing Shielded Bitcoin.
- The Shielded Bitcoin proposal conceals transfer amounts, senders, and receivers using encrypted notes, nullifiers, and zero-knowledge proofs without requiring a Bitcoin soft fork or consensus changes.
- Bitcoin miners and nodes would not validate the shielded state; Bitcoin would instead provide ordering and publication, with the initial profile using OP_RETURN.
- The proposal includes viewing keys allowing selective disclosure to auditors, while transaction timing, fees, and input/output counts would remain visible.
- Peg-in and peg-out mechanisms sit outside the current specification, leaving deposit and withdrawal details unpublished.
- Shielded Bitcoin is a research paper rather than a live product, with Komarov estimating shielded transactions would reach roughly 700 vbytes and quadruple miner fees using experimental witness encryption.
- Researchers have raised questions regarding the scheme's anonymity and quantum resistance, while Bitwise Europe's André Dragosch noted the proposal could be a potential headwind for privacy coins.
Sources · 10 sources
- SO
SolanaFloor@SolanaFloorPost on X ·
NEW: Researchers have proposed Shielded Bitcoin, a way to make private $BTC transfers using Bitcoin L1 without a soft fork. The design hides transfer amounts and counterparties using encrypted notes and zero-knowledge proofs. https://t.co/xRwhPlz7cy
Open source - CO
Cointelegraph@CointelegraphPost on X ·
⚡️ NEW: Researchers at Alloc Init propose "Shielded Bitcoin," a Zcash-style system using zero-knowledge proofs to enable private Bitcoin transfers without a soft fork. https://t.co/nlMOTyG7t5 https://t.co/yK2TLuvn9o
Open source - CT
Coin TelegraphArticle ·
Researchers propose Zcash-style private Bitcoin transfers without a soft fork Shielded Bitcoin would use zero-knowledge proofs and encrypted notes to hide transaction details without changing Bitcoin consensus, but researchers have raised questions about anonymity and quantum resistance.
Open source - CR
CryptoSlate@CryptoSlatePost on X ·
Bitcoin researchers propose Zcash-style private transfers without changing Bitcoin’s consensus rules. The system would hide amounts, senders and recipients while publishing encrypted data on Bitcoin. Bitwise’s André Dragosch sees a potential headwind for privacy coins. But the researchers have not published how BTC would enter or leave the shielded system, leaving the trust and privacy of those transfers unresolved. https://t.co/FetyeHGgfn
Open source - BA
BanklessArticle ·
Alloc Init Proposes Zcash-Style Privacy for Bitcoin The proposed Shielded Bitcoin metaprotocol would use Zcash-style private notes to hide BTC transfers without changing Bitcoin consensus.
Open source - CB
Crypto Banter@crypto_banterPost on X ·
🚨BITCOIN JUST GOT A ZCASH-STYLE PRIVACY PAPER! @allocinitxyz published Shielded Bitcoin. Private transfers on bitcoin:native with no fork and no operators. Same idea Zcash already uses. Encrypted payments, Bitcoin only stores the data. This is a paper, not a live product. Zcash still has the working shielded pool. If Bitcoin ever ships this, privacy demand gets split. Until then the zcash:native thesis holds.
Open source - BC
Bitcoin.com News@BitcoinNewsPost on X ·
JUST IN: 🟠 "Shielded Bitcoin" paper proposes private Bitcoin L1 transfers with no soft fork. Borrows Zcash's encrypted-note/nullifier model, publishes all data on #Bitcoin. Amounts, sender, receiver stay hidden. By [alloc] init. https://t.co/GYeExR6H1H
Open source - UN
UnchainedArticle ·
Bitcoin Could Get Zcash-Style Private Transactions Without a Soft Fork, Misha Komarov Says Misha Komarov , founder of [alloc] init , a firm working on ways to add features such as privacy to Bitcoin without changing its code, said his team is working on “shielded Bitcoin,” a private pool modeled on Zcash that would run on Bitcoin as it exists today, with no soft fork and no company operating it. “It’s basically Zcash,” Komarov said in an interview recorded Sept. 10 for Unchained Premium. Users would deposit bitcoin into the pool, receive an encrypted note they can send, spend or split, and later present that note to withdraw. “We don’t need any soft forks,” he said. Proposals to add new functions to Bitcoin’s code for this kind of feature have not been adopted, Komarov said. His firm’s approach, which it calls Bitcoin PIPEs , instead uses a technique called witness encryption to lock a Bitcoin key that can be unlocked only by someone who proves they followed the rules. The team published the second version of that research in February and has pitched the technique as a way to add privacy, among other features, to Bitcoin’s base layer. This story is brought to you by Unchained Premium . Subscribe to get exclusive interviews, a subscriber-only chat group, and show transcripts. Upgrade Four Times the Fees Each shielded transaction would carry an encrypted note of about 700 vbytes, Komarov said, against roughly 100 to 200 vbytes for a typical Bitcoin transaction. “So we’re talking about four times larger,” he said, with fees to miners rising by the same multiple, which he said is “not catastrophic.” The more people use the pool, the stronger its privacy, he added. Still Experimental “But it’s still pretty experimental,” Komarov said of witness encryption. The encrypted files the scheme depends on remain enormous. [alloc] init said on Sept. 10 that it had cut them to about 8 terabytes, down from roughly 300 terabytes within the past year by Komarov’s account, and it has run open challenges since May inviting researchers to break small instances of the scheme. Shielded pools carry their own risk. Zcash, whose token reached an eight-year high in August, patched a flaw in June that could have let an attacker mint unlimited counterfeit coins. Komarov said the firm plans to reuse tooling that makes its code easier to audit, and rely on repeated audits. He gave no launch date but said that in about a year it would be too late to shape the design, urging Bitcoin users to weigh in now: “the good time to express your opinions on, like, the protocol design is right now.” Related Listen: Zcash, Ethereum, Aztec, Canton and More: Which Chain Will Win the Privacy Race? The post Bitcoin Could Get Zcash-Style Private Transactions Without a Soft Fork, Misha Komarov Says appeared first on Unchained .
Open source - CB
Coin Bureau@coinbureauPost on X ·
🚨HUGE: Bitcoin could get Zcash-style PRIVATE transfers without a soft fork, a new paper proposes. "Shielded Bitcoin" is a new protocol that would hide the amount, sender and receiver of each transfer directly on Bitcoin, while zero-knowledge proofs keep every transfer verifiable. The whitepaper says Bitcoin's transaction history is permanently public, and chain analysis can often link addresses to their owners. With Shielded Bitcoin, users could still share view-only keys with auditors to prove payments
Open source - CR
CryptoSlateArticle ·
Bitcoin researchers target privacy coins with Zcash-style shielded transfers Bitcoin researchers have proposed a system for private transfers directly on the network without requiring a soft fork or changes to its consensus rules. The Sept. 24 paper from [[alloc] init] researchers Clara Shikhelman, Mikhail Komarov, and Aleksei Moskvin introduces Shielded Bitcoin, a metaprotocol designed to conceal transaction amounts, senders, recipients, and links between transfers while publishing its protocol data through Bitcoin mainnet. The design adapts techniques pioneered by Zcash, including encrypted notes, public nullifiers and zero-knowledge proofs, but does not introduce a separate blockchain. Bitcoin instead provides the publication and ordering layer from which participants reconstruct the private transaction state. That would extend Bitcoin privacy beyond existing techniques such as CoinJoin , PayJoin and Silent Payments, which can complicate transaction tracing or reduce address reuse but leave amounts and other transaction details visible. Bitcoin would carry the transactions without validating the privacy layer The proposal avoids waiting for a Bitcoin upgrade by moving the privacy logic above the network’s consensus rules. Users would hold BTC-denominated value as encrypted notes. When funds are transferred, the sender would publish an envelope containing encrypted outputs, public nullifiers marking previously held notes as spent, and a zero-knowledge proof establishing ownership and value conservation. The amount being transferred and the identities of the counterparties would remain hidden. Bitcoin miners and nodes would not validate the shielded state themselves. Instead, implementations following the Shielded Bitcoin rules would scan BTC blocks and replay accepted transfer envelopes in their recorded order, producing a common note tree and spent-note set. Bitcoin would therefore provide the timestamped transaction history and ordering needed to reconstruct the system, while the metaprotocol would handle encrypted balances and transfer verification. The current implementation profile uses OP_RETURN to publish the encrypted transfer data, though the researchers leave open the possibility of other publication methods. That architecture differs from Zcash, where the network’s consensus rules enforce shielded transaction validity directly. Shielded Bitcoin would keep BTC consensus untouched while deriving a separate private state from data anchored to the chain. Some metadata would remain visible. Transaction timing, fees, input and output counts, and characteristics of the Bitcoin transaction carrying the encrypted data could still give observers clues. The paper also includes viewing capabilities that could allow users to selectively disclose transaction information without surrendering control of their funds, creating a route for auditing or compliance where required. Sam Callahan, the director of strategy and research at Bitcoin treasury company OranjeBTC, said the development fits a broader view that Bitcoin can accumulate functionality without competing with other blockchains feature by feature. Callahan said : “People still misunderstand Bitcoin’s moat. Bitcoin doesn’t need to win every feature race. Privacy, speed, and functionality can be built over time. The moat is its decentralization, security, and credible monetary policy,” he added. “And on those dimensions, nothing else comes close.” The design remains incomplete at one critical boundary: moving ordinary BTC into and out of the shielded system. Peg-in and peg-out mechanisms sit outside the current specification. Those components would need to lock Bitcoin on mainnet, represent that value inside the private note system, and later release the corresponding BTC when users exit. [[alloc] init] expects those flows to rely on its PIPEs v2 work, but the researchers have yet to publish the detailed construction. That leaves open questions around whether entry and exit can be made trustless, private, and resistant to transaction linkage. A distinctive deposit amount, withdrawal amount, or timing pattern could still connect activity at either end of the shielded system. Other deployment choices also remain unresolved, including the final proof system, publication format, and how light clients can verify shielded state without replaying the full relevant Bitcoin history. Privacy coins face fresh pressure as Zcash rally tests the thesis The proposal comes as privacy-focused cryptocurrencies again attract investor attention, reviving a long-running debate over whether dedicated privacy networks retain an enduring technological advantage over Bitcoin. André Dragosch, Bitwise Europe Head of Research, described Shielded Bitcoin as a “potential headwind for privacy coins,” reflecting the risk that features once associated with separate networks could increasingly be reproduced around Bitcoin without altering its monetary rules or base-layer consensus. That argument becomes more consequential for Zcash, where privacy has become central to the token’s recent revaluation. ZEC climbed above $1,600 this week as shielded activity accelerated and investors returned to the idea that Zcash offers native transactions that can conceal senders, recipients, and amounts. Usage has moved alongside price. Weekly shielded transactions recently reached 62,379, their highest level since 2022, while nearly 5 million ZEC were held in shielded pools this month. The network also settled more than $23 billion in transfer volume last week, its strongest weekly total since 2021. Shielded Bitcoin pressures that narrative because it seeks to deliver comparable transaction confidentiality while keeping BTC as the underlying asset. If the system eventually works as designed, users seeking stronger privacy would have another route besides moving into a dedicated privacy coin. The post Bitcoin researchers target privacy coins with Zcash-style shielded transfers appeared first on CryptoSlate .
Open source