

NEAR Intents recovers full $3.8 million after issuing 48-hour ultimatum to hacker
Cross-chain protocol NEAR Intents recovered all $3.8 million drained in an Oct. 1 exploit after leadership publicly identified the attacker and issued a 48-hour deadline.
Cross-chain trading protocol NEAR Intents has recovered the full $3.8 million drained during an Oct. 1 exploit, concluding its investigation after publicly confronting the attacker. General manager Alex Shevchenko posted Bitcoin, BNB/Ethereum, and Solana return addresses alongside a 48-hour deadline for responsible disclosure, telling the perpetrator publicly, "We have identified you, sir."[2][3][4][7]
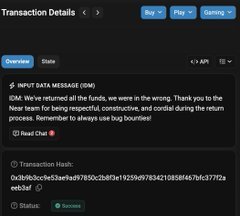
Roughly 14 to 15 hours after the ultimatum was issued, the attacker returned the funds. On-chain transfers delivered about 34.6 BTC to the Bitcoin address, which researcher Kuncoro calculated accounted for around 78% of the loss, with Shevchenko confirming the remainder came back separately. A transaction to the BNB/Ethereum address included an on-chain message stating, "We've returned all the funds, we were in the wrong," while thanking the team for being respectful and urging protocols to rely on bug bounties instead.[4][5][6]
NEAR co-founder Illia Polosukhin credited internal detective work and the platform's SHIELD AI security layer with tracking down the attacker in under 24 hours. The incident stemmed from a vulnerability in how the Omni deposit and withdrawal infrastructure interacted with the NEAR Intents smart contract, confined to USDT on BNB Smart Chain. Polosukhin stated that the issue was patched in less than an hour and that the broader NEAR blockchain and native token were unaffected.[1][4]
Key facts
- NEAR Intents recovered the full $3.8 million drained during an exploit on Oct. 1 and subsequently closed its investigation.
- General manager Alex Shevchenko publicly posted Bitcoin, BNB/Ethereum, and Solana addresses and set a 48-hour deadline after announcing the attacker had been identified.
- The exploiter returned the funds about 14 to 15 hours after Shevchenko published the ultimatum.
- The attacker left an on-chain transaction message admitting they were in the wrong, thanking the team, and advocating for the use of bug bounties.
- The exploit was caused by a flaw in the Omni deposit and withdrawal interaction with the protocol's smart contract on BSC USDT, which was patched within an hour.
- NEAR co-founder Illia Polosukhin credited the SHIELD AI security layer and internal team investigation for discovering the attacker's identity in under 24 hours.
Sources · 6 sources
- CB
Crypto BriefingArticle ·
NEAR Intents GM addresses $3.865 million exploit tied to Omni bug The swift recovery and patching highlight the importance of transparency and rapid response in maintaining trust in DeFi systems. The post NEAR Intents GM addresses $3.865 million exploit tied to Omni bug appeared first on Crypto Briefing .
Open source - DE
DecryptArticle ·
'We Have Identified You, Sir': Near Intents Recovers $3.8 Million After 48-Hour Ultimatum Near Intents said the roughly $3.8 million drained in an exploit on Thursday was returned in full, a day after the team said it had identified the attacker and gave them 48 hours to return the funds.
Open source - CB
Crypto BriefingArticle ·
NEAR Intents recovers $3.8 million from exploit and closes its investigation The incident underscores the vulnerability of cross-chain protocols, highlighting the need for robust security measures and rapid response strategies. The post NEAR Intents recovers $3.8 million from exploit and closes its investigation appeared first on Crypto Briefing .
Open source - UN
UnchainedArticle ·
NEAR Intents Says Exploited $3.8 Million Is Back, Closes Its Hack Investigation NEAR Intents , the cross-chain trading protocol hit by a $3.8 million exploit on Oct. 1, got all of the money back from the attacker on Friday and closed its investigation. “The funds from the $3.8M NEAR Intents hack were sent back in full,” general manager Alex Shevchenko wrote on X. “We are stopping the investigation.” The return came roughly 14 hours after Shevchenko called out the attacker in public and posted Bitcoin, BNB/Ethereum and Solana addresses for the funds. “We have identified you, sir,” he wrote, telling the attacker they knew “better than most how responsible disclosure works” and had 48 hours to use it. Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . Funds Came Back Onchain The Bitcoin address Shevchenko listed took in about 34.6 BTC over several transfers between 14:31 and 15:05 UTC on Friday, according to blockchain data. That did not cover the whole loss. An onchain researcher who goes by Kuncoro estimated the bitcoin was worth about 78% of the $3.8 million and asked whether the rest came back another way. “You are right. It did indeed,” Shevchenko replied , without saying how. About an hour after the bitcoin arrived, a transaction to the BNB/Ethereum address carried a note in its data field: “We’ve returned all the funds, we were in the wrong.” NEAR co-founder Illia Polosukhin said the team identified “the party responsible less than 24h after the hack, established communication, and got the funds back in full” at 14:30 UTC. He credited SHIELD , the AI security layer on Intents, “along with some aggressive detective work.” Asked who did the tracing, Shevchenko answered “Internal team.” Neither executive detailed how the attacker was found. A Bug in Omni Deposits and Withdrawals NEAR Intents halted its services on Oct. 1, blaming “a bug in the Omni deposit and withdrawal infrastructure interaction with NEAR Intents smart contract.” It pledged to make affected users whole and said a detailed report would follow. Polosukhin wrote that day that the flaw was confined to USDT on BSC and was patched in under an hour, and that the NEAR blockchain and its token were unaffected. He said Intents handles more than $4 billion a month in trading and payments, and called this its first major exploit. The hack hit days after NEAR Intents blocked stolen Bitget funds from moving through the protocol. Shevchenko asked hackers to “use bug bounties instead of disrupting the services,” and Polosukhin echoed him. “They exist for a reason,” he wrote. Related Listen: How Bitget Is Chasing $388 Million in Stolen Funds After a Zero-Day Hack The post NEAR Intents Says Exploited $3.8 Million Is Back, Closes Its Hack Investigation appeared first on Unchained .
Open source - BL
BlockNews@blocknewsdotcomPost on X ·
🚨 UPDATE: The full $3.8 MILLION stolen in the NEAR Intents hack has been returned. 🔥 NEAR Intents GM Alex Shevchenko says all funds have been recovered and the investigation is now being closed. The hacker wrote in the return transaction: “We've returned all the funds, we were in the wrong… Remember to always use bug bounties!”
Open source - CN
crypto.news@cryptodotnewsPost on X ·
BREAKING: NEAR Intents hacker returns all $3.8M stolen in Thursday’s exploit The attacker sent the full amount back about 15 hours after the team identified them and set a 48-hour deadline, bringing the investigation to a close. https://t.co/UOMEeTNM2L
Open source - KO
kook@KookCapitalLLCPost on X ·
near intents just got the whole $3.8m back thursday a bug in the omni deposit/withdrawal layer let someone drain the cross-chain swap desk friday alex shevchenko posts the funds are returned in full and the investigation is over the move that printed was not a quiet backchannel it was a public post with return addresses across btc bnb/eth and solana and the line that made ct lose it we have identified you sir 48 hours return the funds or the window for responsible disclosure closes law enforcement already looped in zachxbt had the stolen pile hitting kucoin and bridging to btc then an on-chain note that looks like the exploiter weve returned all the funds we were in the wrong please use bug bounties instead of disrupting the services same week near intents already blocked a ~$50m swap attempt tied to the bitget ~$387m drain that bitget and elliptic pinned on north korea so the desk that stopped nk from washing fifty through intents got hit two days later by a different attacker..... and still collected every dollar back by naming them in public this is a $30b+ volume intents rail across 35 chains bitwise spot near etf just started trading and the recovery meta that actually works right now is not hope and vibes it is identify ultimatum make the return cheaper than running we find out
Open source