

Keystone breach exposes customer records and device authentication key, prompting destruction of nearly 19,000 wallets
Hardware wallet maker Keystone disclosed a website breach that leaked nearly 26,000 customer purchase records and compromised a WebAuth device-verification key, forcing the company to destroy 18,835 unsold units.
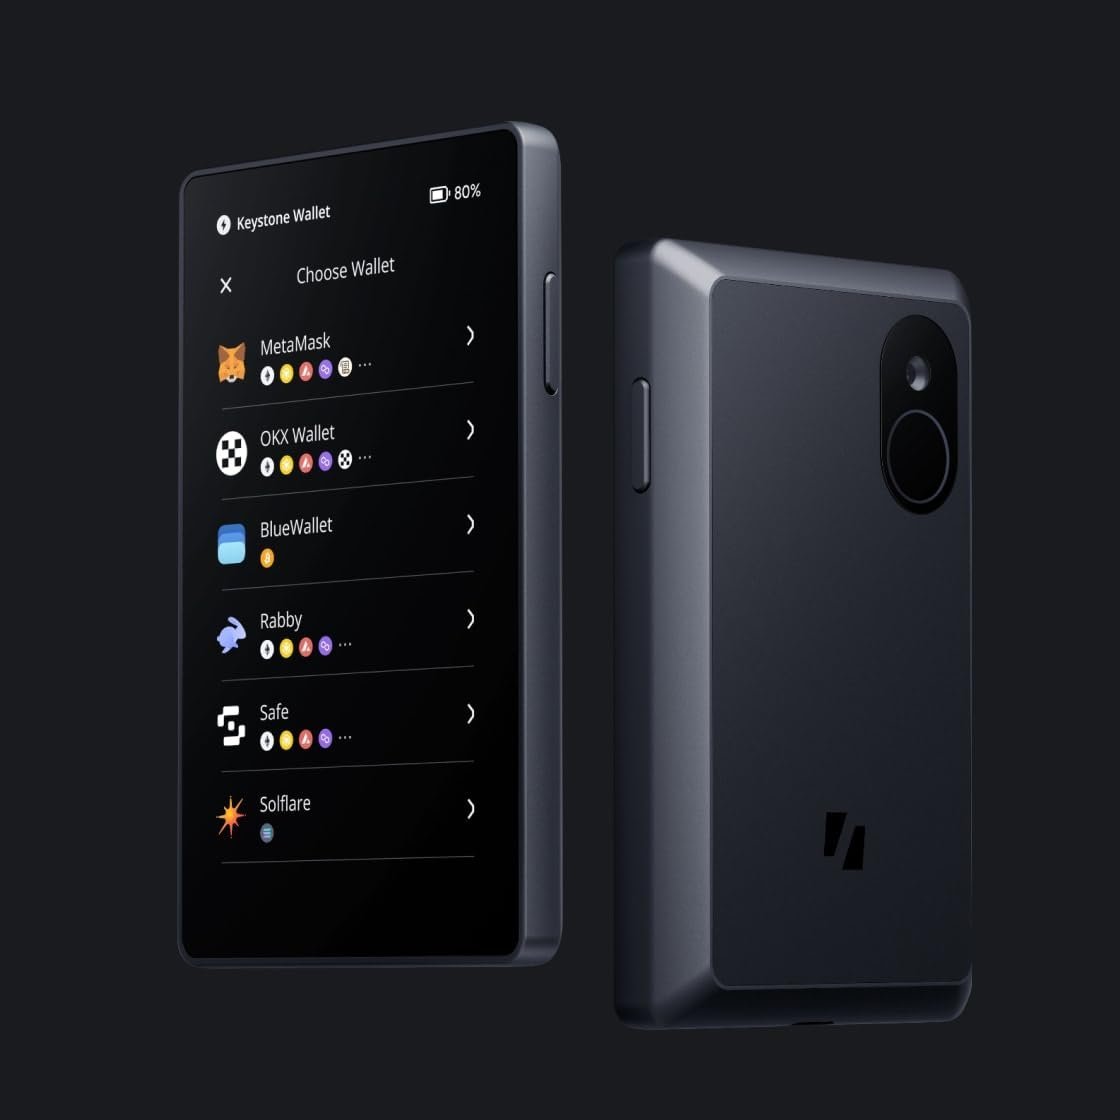
Hardware wallet manufacturer Keystone disclosed that an intruder breached its official website, compromising customer shipping details along with a critical device-authentication key. The stolen WebAuth key, which is used to verify that hardware units are genuine, could potentially allow counterfeit devices to pass official authenticity checks. In response, Keystone suspended shipments, announced that new production will transition to a replacement key, and confirmed it will destroy 18,835 unsold devices carrying the compromised key.[1][2][4][7][11]
According to Keystone, the breach affected 25,964 completed purchase records and 12,873 incomplete checkout entries from its Shopify store. The compromised information includes customer names, contact information, shipping addresses, purchased products, and prices paid. The company stated that sensitive payment card and banking details, recovery phrases, private keys, wallet passwords, and transaction signing remained secure.[1][4][5][10]
Keystone detected unauthorized activity on its website on October 20 and confirmed the intrusion on October 23 after reviewing API logs with Shopify. The public disclosure followed reports from a user who received a social engineering call citing Keystone purchase details from 2024. While Keystone had previously stated that shipping data is automatically erased 180 days after an order, the firm acknowledged that its automated deletion tool had not functioned reliably, leading to data being retained longer than intended.[1][5][6]
Keystone warned customers to stay vigilant against fraudulent communications from impersonators offering fake refunds, replacement hardware, or order fixes. The company also noted that it cannot fully rule out counterfeit devices among units delivered after October 20.[1][5][7]
Key facts
- Attackers breached Keystone's website and obtained a WebAuth device-authentication key used to verify whether hardware wallets are genuine.
- Keystone will destroy 18,835 unsold hardware wallets in its inventory that rely on the compromised key and paused pending shipments.
- The incident exposed 25,964 purchase records and 12,873 incomplete checkout records, including names, contact details, shipping addresses, and purchased items.
- Keystone stated that recovery phrases, private keys, wallet passwords, and payment card details were not exposed.
- Keystone detected the website intrusion on October 20 and confirmed the data exposure on October 23 after verifying API logs with Shopify.
- Keystone conceded that its automated deletion tool failed to operate reliably, retaining customer data past its stated 180-day deletion policy.
- Keystone said it cannot fully rule out counterfeit devices among units received after October 20.
Sources · 9 sources
- PR
ProtosArticle ·
Keystone to destroy almost 19,000 wallets after device key leak Keystone says it will destroy almost 19,000 unshipped hardware wallets after an attacker obtained the key it uses to verify its devices. First, Keystone took to X on Saturday to confirm a suspected breach of customer shipping information, including “names, contact details, shipping addresses, and order details (items and prices).” The confirmation came around 18 hours after a customer reported a “social engineering” call in which Keystone order information was used. While sensitive payment information and wallet keys were not involved, the firm did warn against scammers impersonating its staff and “offering refunds, replacement devices, or ‘fixes’ for your order or address.” We owe you an apology. On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we… — Keystone Hardware Wallet (@KeystoneWallet) October 24, 2026 Read more: Ledger says Southeast Asia reseller linked to $86M draining The company had previously promised that “180 days after your order, your shipping data is permanently deleted,” but the user that initially flagged the potential data breach claims that their device was purchased in 2024. A later update put the total number of affected records at almost 26,000, limited to purchases made via Shopify on its official site (plus a further 13,000 incomplete purchase records of partial order information). It also states that another 25,000 records had already been “permanently erased… in accordance with our data retention policy.” However, it concedes that its automated data deletion tool “did not operate reliably… resulting in certain personal information being retained beyond the permitted period.” Worryingly, the update also included the admission that “the attacker also obtained the WebAuth key we use to verify whether a device is genuine. ” Newly built Keystone wallets will use a new key, with shipping suspended pending the change, and almost 19,000 units of existing un-shipped inventory will be destroyed. Foundation Passport: botched data migration Similarly, reports of phishing emails targeting Foundation Passport users circulated on X from early Monday morning. Screenshots show the use of scare tactics regarding a display module, undoubtedly inspired by the recent compromised Ledger devices. The manufacturer confirmed that the “spam” emails had been sent from its official domain and traced the source to “one or more compromised API keys on Cloudflare.” Read more: Ledger roasted over $849 device launch after $86M hack Foundation, too, had previously assured users that customer data is “automatically” deleted after 60 days. In an update , it clarified that over 20,000 phishing attempts were delivered across its systems, but that they “are still determining” how many users had their personal data exposed. As to the data deletion within 60 days, it claims that its previous provider WooCommerce did purge order data. However, “during past database migrations,” only the new tables were redacted, while “older copies still contained personal information.” It adds that more recent orders placed via Shopify “may also have been exposed.” (Dis)honourable mentions Hardware wallet users have had it rough in recent weeks, to put it lightly. While cold storage has always been seen as the safest option for crypto users to store their assets, a series of security incidents has seen hefty losses as well as data leaks that will have users looking over their shoulder for years to come. Between them, Ledger’s spyware scandal and Coldcard’s seed generation bug led to over $200 million in losses. We are investigating how a post containing a phishing link was published from this account. It has since been deleted. Do not visit or interact with that link. COLDCARD’s only official website is https://t.co/veUyheguQW . This account has used offline 2FA with tightly restricted… pic.twitter.com/bLwwUb1CVu — COLDCARD (@COLDCARDwallet) October 11, 2026 Read more: Trezor’s summer of hacks continues with Brevo email breach Other recent leaks have come from repeat offender Ledger , its primary competitor, Trezor , and SafePal . Fresh off the back of devastating user losses, Coldcard had its X profile compromised to publish a phishing scam to its 67,000 followers earlier this month. While not a data leak, per sé, it was especially embarrassing coming just two days after an attempt to capitalize on Ledger’s bad press with a ballsy tweet about its wallet’s clear case. Got a tip? Send us an email securely via Protos Leaks . For more informed news and investigations, follow us on X , Bluesky , and Google News , or subscribe to our YouTube channel . The post Keystone to destroy almost 19,000 wallets after device key leak appeared first on Protos .
Open source - BA
Bankless@BanklessPost on X ·
NEWS: Keystone says the attacker behind its Oct. 20 store breach also took the key it uses to verify its wallets are genuine. It will destroy the 18,835 wallets in its inventory that carry that key. The breach exposed 25,964 buyer records, including names and addresses. https://t.co/BhcH2zdoXk
Open source - CB
Crypto Briefing@Crypto_BriefingPost on X ·
🚨NEW: Keystone is investigating unauthorized website access that exposed customer names, contact details, shipping addresses and order information. The company says payment card and bank information, recovery phrases, private keys and wallet passwords were not affected. https://t.co/DQcPdhKu1g
Open source - WB
Wu Blockchain@WuBlockchainPost on X ·
Keystone Breach Exposed 25,964 Purchase Records and Compromised Device Verification Key Keystone said its latest investigation found that attackers obtained a WebAuth device-authentication key through the website breach, potentially allowing counterfeit hardware wallets to pass official authenticity checks. The company will destroy 18,835 unsold devices using the old key, pause unshipped orders and switch new production to a replacement key. The incident also affected 25,964 purchase records and 12,873 incomplete checkout records, while Keystone said seed phrases, private keys and transaction signing were not compromised.
Open source - UN
UnchainedArticle ·
Keystone Says Intruder Took Customer Names and Addresses From Its Website Keystone is warning customers that an intruder got into its official website and took their shipping information , the company said in an Oct. 24 post on X . Keystone said it detected the intrusion on Oct. 20 and, after checking API activity with Shopify , the e-commerce platform behind its store, confirmed on Oct. 23 that the data had been taken. “We owe you an apology,” the company wrote. According to Keystone, the exposed records include customers’ names, contact details, shipping addresses and order details , covering the items bought and the prices paid. The company said payment card and bank details, recovery phrases, private keys and wallet passwords were not part of the exposure. Keystone said it has cut off the access, patched the flaw, opened an investigation and begun emailing affected customers. Its post did not say how many customers were affected, how the intruder got in, or what range of order dates the data covered. Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . What Keystone Says About Data Retention Keystone has described its handling of shipping data in several places over the years. The earliest is the company’s privacy policy , last updated May 15, 2021 . It says Keystone wipes order information for any customer who has gone 180 days without placing an order, and that its retention practice follows Shopify’s policy. A Keystone help center article , updated in February 2023 , presents deletion of shipping data older than 180 days as something customers must request, confirming they have no order disputes and supplying the email address used for the order, a process it says can take two to three weeks. The article says “records of the customer’s city and country will not be deleted,” and that Shopify performs the final deletion. In a Jan. 5 post on X , which quoted ZachXBT’s alert about a Ledger customer-data leak through payment processor Global-e, Keystone wrote that “180 days after your order, your shipping data is permanently deleted.” Its Privacy Promises page likewise says shipping details are removed automatically 180 days after an order is placed, and that buyers can ask for deletion as soon as their device arrives. Keystone Warns of Impersonators The company warned that scammers could pose as Keystone by phone, text, email or post, offering refunds, replacement devices or order fixes. It told users never to share a recovery phrase or type one into a device they did not order. Keystone said a detailed report on the breach is coming soon. Related Listen: Why a $100M Ledger Reseller Attack Has Crypto Rethinking Self-Custody The post Keystone Says Intruder Took Customer Names and Addresses From Its Website appeared first on Unchained .
Open source - TB
The Block@TheBlockCoPost on X ·
THE BLOCK: Hardware wallet maker Keystone says an attacker accessed customer names, addresses and order details via its Shopify store. Keystone has said it deletes shipping data after 180 days, but some customers claim they were targeted from older orders. https://t.co/tz75jadhCU
Open source - BA
BanklessArticle ·
Keystone Breach Widens as Attacker Grabs Its Device Authentication Key The hardware wallet maker will destroy 18,835 old devices and says it can't fully rule out fakes among units received after Oct. 20th.
Open source - CT
Coin TelegraphArticle ·
Keystone breach deepens: Hackers stole key used to verify wallets as genuine Keystone initially disclosed a leak of customer information but has since disclosed that hackers also stole a key that could allow counterfeit wallets to pass authenticity checks.
Open source - SI
Solid Intel 📡@solidintel_xPost on X ·
INTEL: Keystone reveals hackers stole customer data and a key used to authenticate its hardware wallets, forcing the destruction of 18,835 devices and suspension of shipments https://t.co/4lSjMi7VzP
Open source - WB
Wu Blockchain@WuBlockchainPost on X ·
Keystone Confirms Customer Data Exposure Following Unauthorized Website Access Keystone Hardware Wallet confirmed that a third party obtained customer shipping and order information following unauthorized access to its official website. The incident was detected on October 20, with the data exposure confirmed on October 23 after reviewing API activity with Shopify. Exposed information included names, contact details, shipping addresses, purchased items, and prices. Payment card and bank details, recovery phrases, private keys, and wallet passwords were not exposed. Keystone said it has blocked the access, fixed the vulnerability, and is notifying affected customers. It also warned of impersonation scams involving fake refunds, replacement devices, or order fixes.
Open source - CB
Crypto Briefing@Crypto_BriefingPost on X ·
🔐TODAY: Crypto hardware wallet maker Keystone disclosed a security breach exposing 25,964 customer records and a device authentication key that could allow counterfeit wallets to pass verification. The company will destroy 18,835 devices and suspend shipments. Private keys and recovery phrases were not compromised.
Open source