

Passport hardware wallet maker Foundation hit by phishing attack via compromised Cloudflare API keys
Hardware wallet maker Foundation said attackers compromised its Cloudflare API keys and backend infrastructure to send phishing emails from official domains, though it emphasized that Passport hardware and customer funds remain safe.
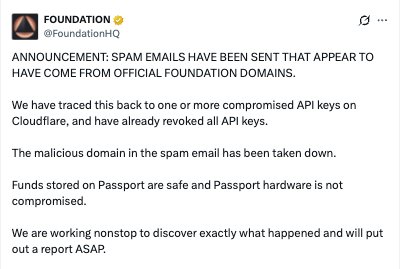
Foundation, the maker of the Passport bitcoin hardware wallet, announced that attackers sent phishing emails disguised as official communications after compromising one or more of the company's Cloudflare API keys. The company stated that it promptly revoked all API keys, took down the malicious domain referenced in the emails, and confirmed that Passport hardware devices and funds stored on them remain secure and uncompromised.[2][3]
According to Foundation CEO Zach Herbert, attackers breached backend infrastructure through a vulnerability in a self-hosted application, which likely allowed them to access the company's customer support inbox. Herbert said the team cut off the attackers' email access within 10 minutes of receiving user reports and removed them from internal systems. He added that Foundation plans to publish a formal report once its investigation concludes.[3]
Recipients reported receiving emails—some framed as fake Passport recall notices or warnings stating "Your Passport funds are at risk"—that included their real names, physical addresses, phone numbers, and past purchase details. The messages directed users to malicious sites attempting to harvest wallet seed phrases. Herbert noted that customer personal details appear to have been sourced from the support inbox, other recent cryptocurrency data leaks, and potentially recent orders from Foundation's new Shopify store.[1][3]
Key facts
- Phishing emails were sent appearing to originate from official Foundation domains.
- Foundation traced the unauthorized emails to one or more compromised Cloudflare API keys and revoked all API keys.
- Foundation stated that Passport hardware is not compromised and funds stored on the devices are safe.
- CEO Zach Herbert reported that backend infrastructure was breached through a vulnerability in a self-hosted app, likely exposing the customer support inbox.
- Foundation cut off the attackers' ability to send emails within 10 minutes of user reports and took down the malicious domain.
- The phishing emails included customer names, addresses, and purchase information, directing recipients to external sites prompting them to enter seed phrases.
Sources · 3 sources
- BC
Bitcoin.com News@BitcoinNewsPost on X ·
🚨 HOT OFF THE WIRE: Hardware Wallet Maker Foundation Hit by Phishing Attack as Hackers Hijack Official Email Domains, Send Fake Passport Recalls and Target Customers With Real Names, Home Addresses and Purchase Details. https://t.co/mClZ5vVFui
Open source - CO
Cointelegraph@CointelegraphPost on X ·
🚨 ALERT: Foundation warns spam emails were sent from its official domains via compromised Cloudflare API keys, but says Passport funds and hardware remain safe. https://t.co/5LiDiCzYQQ
Open source - UN
UnchainedArticle ·
Passport Wallet Maker Foundation Traces Phishing Emails to Backend Breach, Promises Report Foundation , the company behind the Passport bitcoin hardware wallet, said customer funds and devices are safe after attackers sent phishing emails that looked like they came from its official domains and steered recipients toward giving up their seed phrases . The company announced the incident on X late Sunday U.S. time. It said it had traced the emails to “one or more compromised API keys on Cloudflare” and had “already revoked all API keys.” The malicious domain linked in the messages had been taken down, Foundation said in the post, adding that “funds stored on Passport are safe and Passport hardware is not compromised.” Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . The CEO’s Account About two hours later, CEO Zach Herbert wrote in a post on X that “some of our backend infrastructure was compromised via a vulnerability in a self hosted app,” and that attackers “were likely able to compromise our customer support inbox.” Herbert said the team cut off the attackers’ ability to send email “within 10 minutes of user reports” and removed them from its systems. Some of the emails included customers’ mailing addresses or phone numbers . Herbert said the company believes that information came from the support inbox, from data attackers pulled in from “other recent crypto leaks” and possibly from recent orders on Foundation’s new Shopify store. What Recipients Saw One recipient, X user @tuxpizza, posted that the message arrived from Foundation’s official address, carried their real name and address, and linked to an outside site that “tries to make you paste your seed phrase into their web wallet.” MyCrypto founder Taylor Monahan said the email reached her inbox without being caught as spam and appeared to reference a mid-2025 purchase, along with a name, email and shipping address. Foundation’s blog now carries a banner warning that emails saying “Your Passport funds are at risk” are a scam and telling users not to share their recovery phrase. The company has not said how many customers received the emails. Herbert wrote that Foundation would “share a formal report when we have all details” and release more information “tomorrow,” adding, “I’m very sorry.” Related Listen: Why a $100M Ledger Reseller Attack Has Crypto Rethinking Self-Custody The post Passport Wallet Maker Foundation Traces Phishing Emails to Backend Breach, Promises Report appeared first on Unchained .
Open source