

Cursor flags malicious Claude Code extension affecting up to 5,000 users
AI coding tool Cursor detected a tampered version of the Claude Code VS Code extension in its marketplace that attempted to install an SSH backdoor, potentially impacting up to 5,000 developers.
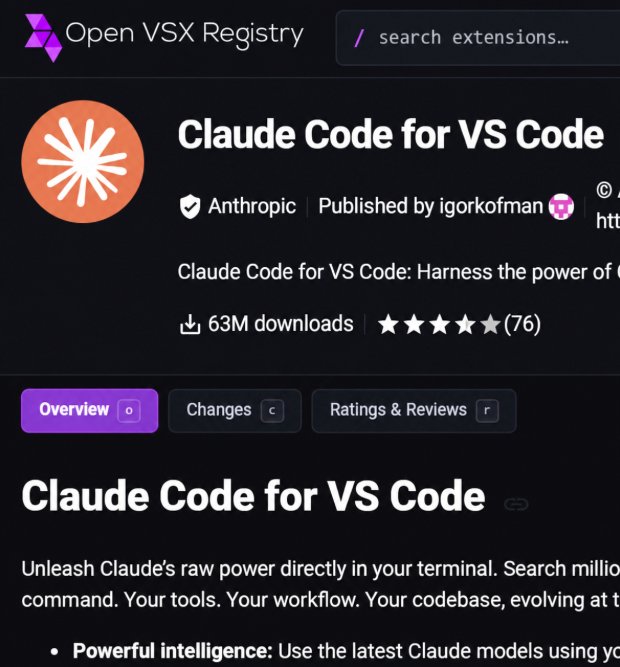
Cursor reported a cybersecurity incident after uncovering an unauthorized, backdoored copy of the Claude Code extension on its marketplace. The malicious package was available for roughly 11 to 12 hours on Thursday and potentially affected up to 5,000 users, particularly those with automatic updates turned on.[1][2][3][4][8]
The counterfeit extension attempted to establish remote access by installing an SSH backdoor and sought to gather sensitive device details, usernames, and public IP addresses. Anthropic confirmed that it neither built nor published the tampered release, explaining that an attacker abused access to Cursor's marketplace to distribute the compromised software.[1][2][5][6][7]
In response, Cursor pulled the rogue package, rebuilt its marketplace, and helped take down the attacker's server. Other marketplace offerings, including Grok Bot, Grok, and related SpaceXSI products, were not compromised during the incident.[2][5][8]
Anthropic issued a legitimate version 2.1.314 update across Open VSX and Microsoft's VS Code Marketplace on October 30. Impacted developers are urged to install the official update, rotate their credentials, and follow Cursor's remediation protocols, as merely uninstalling the rogue extension may not completely eradicate the malware.[8]
Key facts
- Cursor uncovered a malicious copy of the Claude Code VS Code extension that may have impacted up to 5,000 users.
- The tampered extension attempted to install an SSH backdoor, collect usernames, device details, and public IP addresses, and provide remote computer control.
- The backdoored extension remained listed in Cursor's marketplace for roughly 11 to nearly 12 hours.
- Anthropic stated it did not develop or publish the tampered extension and noted that an attacker used access to Cursor's marketplace to release it.
- Cursor removed the malicious package, rebuilt its marketplace, and aided in taking the attacker's server offline.
- Other extensions on the marketplace, including Grok Bot, Grok, and other SpaceXSI products, were not affected.
- Anthropic released update 2.1.314 on Open VSX and Microsoft's VS Code Marketplace on October 30.
- Users are advised to rotate credentials and follow cleanup instructions, as uninstalling the extension alone may not remove the malware.
Sources · 8 sources
- CB
Crypto Briefing@Crypto_BriefingPost on X ·
💥ICYMI: Cursor identifies a malicious Claude Code extension that attempted to install an SSH backdoor and potentially affected up to 5,000 users. https://t.co/OKJoJIkQYj
Open source - DE
Decrypt@DecryptMediaPost on X ·
Malicious Claude Code Extension Hit Up to 5,000 Cursor Users. A tampered version of the extension, not made by Anthropic, sat in Cursor's marketplace for about 11 hours Thursday and tried to install an SSH backdoor. Cursor says it pulled it, rebuilt the marketplace and helped take the attacker's server offline.
Open source - CO
Cointelegraph@CointelegraphPost on X ·
🚨 ALERT: Cursor reports a security incident involving a malicious Claude Code VS Code extension that may have affected up to 5,000 users. This malicious version of the extension was not developed by Anthropic. https://t.co/CIEFZD3CZV
Open source - AT
Ars Technica@arstechnicaPost on X ·
Anthropic VS code extension on Cursor backdoored for nearly 12 hours https://t.co/6ux4ePLGn9
Open source - AI
Analytics Insight@analyticsinmePost on X ·
𝗖𝘂𝗿𝘀𝗼𝗿 𝗖𝗹𝗮𝘂𝗱𝗲 𝗖𝗼𝗱𝗲 𝗘𝘅𝘁𝗲𝗻𝘀𝗶𝗼𝗻 𝗛𝗮𝗰𝗸 𝗥𝗲𝗽𝗼𝗿𝘁𝗲𝗱𝗹𝘆 𝗔𝗳𝗳𝗲𝗰𝘁𝘀 𝟱,𝟬𝟬𝟬 𝗨𝘀𝗲𝗿𝘀 A malicious code extension may have put 5,000 Cursor users at risk! The tampered Claude Code extension reportedly attempted to collect usernames, device details, and public IP addresses while establishing remote access. Cursor has removed the extension and rebuilt its marketplace, but how safe are your AI coding tools? This incident raises fresh cybersecurity concerns. #Cursor #ClaudeCode #CyberSecurity #AI #TechNews #DataSecurity #AnalyticsInsight #AnalyticsInsightMagazine Read More 👇 https://t.co/1hwxzK6lDo
Open source - TE
Techmeme@TechmemePost on X ·
Anthropic says a malicious actor used access to Cursor's marketplace to publish a "tampered" copy of the Claude Code extension, which it didn't build or publish (@felixrieseberg) (Visit Techmeme dot com for the link and full context!)
Open source - PO
Polymarket@PolymarketPost on X ·
BREAKING: Cursor discovers a malicious version of Claude Code in its marketplace that attempts to give hackers remote access to users' computers, potentially affecting up to 5,000 users.
Open source - CB
Coin Bureau@coinbureauPost on X ·
🚨ALERT: Up to 5,000 users affected after a malicious Claude Code extension appeared on Cursor’s marketplace. Cursor is an AI coding tool that helps developers write and edit software. Users with auto-updates enabled could have downloaded it. Cursor says the malicious version was not developed by Anthropic. Other marketplace extensions, Grok Bot, Grok and its other SpaceXSI products were not affected. Cursor REMOVED the package and took the attacker’s server offline. As of October 30, Anthropic has released 2.1.314 update on Open VSX and Microsoft’s VS Code Marketplace. Users SHOULD update. Those affected also need to follow Cursor’s cleanup steps and rotate credentials. Uninstalling alone may NOT REMOVE the malware.
Open source