

Microsoft links China-aligned Storm-0940 to AI-driven ConnectWise breach
Hackers linked to China used an AI penetration testing framework called ARTEX to compromise ConnectWise and target hundreds of organizations worldwide, according to Microsoft.
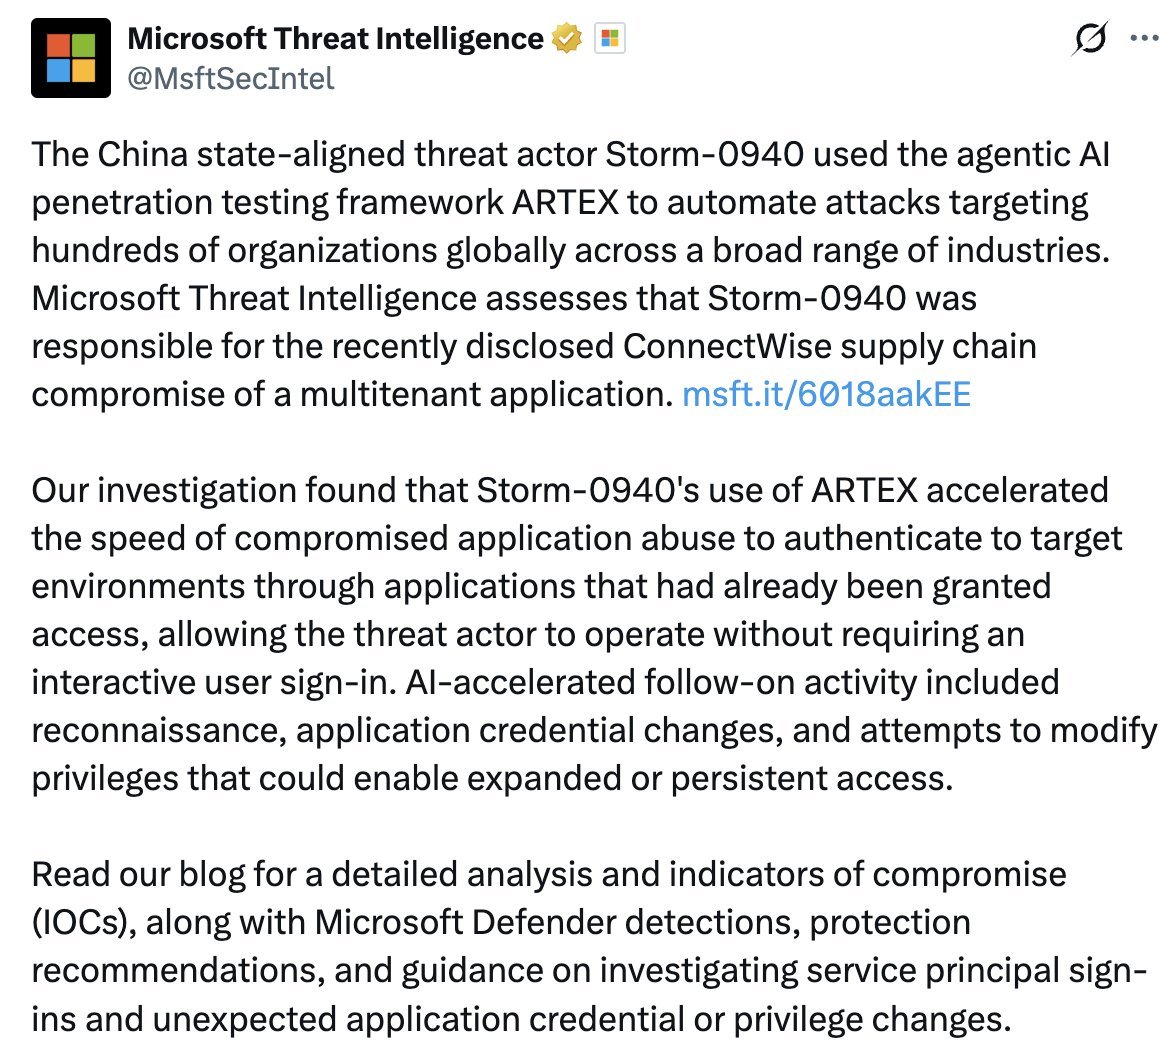
A China-aligned cyber threat group identified as Storm-0940 compromised IT management provider ConnectWise as part of an attack targeting hundreds of organizations globally, according to Microsoft. The campaign leveraged ARTEX, an AI-driven penetration testing framework that uses agentic AI to automate and accelerate intrusions across victim networks.[1][4][5][7][8][10]
The intrusion did not rely on a newly developed exploit, but instead abused a compromised, over-permissioned ConnectWise OAuth application. Using automated AI agents, the attackers executed sign-in attempts across more than 2,250 cloud tenants at a rate of approximately 2,900 attempts per minute, enabling them to gain privileged cloud access in under three hours in several cases.[2][3][6][9]
Microsoft cautioned that the speed of the AI-driven campaign highlights the growing need for organizations to implement enhanced cloud security defenses and ensure faster human incident response capabilities.[4][7]
Key facts
- Microsoft attributed the breach of IT services firm ConnectWise to the China-linked threat group Storm-0940.
- The threat actor utilized ARTEX, an AI-driven penetration testing framework featuring agentic AI capabilities.
- The attack targeted hundreds of organizations globally and signed into more than 2,250 cloud tenants.
- The automated operation reached a pace of roughly 2,900 sign-in attempts per minute.
- Attackers exploited a compromised, over-permissioned ConnectWise OAuth application rather than a new software vulnerability.
- The intrusion achieved privileged cloud access in under three hours in multiple instances.
Sources · 9 sources
- TE
Techmeme@TechmemePost on X ·
Microsoft says China-linked hackers used AI penetration testing tool ARTEX to compromise ConnectWise as part of a campaign targeting hundreds of organizations (@ajvicens / Reuters) (Visit Techmeme dot com for the link and full context!)
Open source - CH
Chubby♨️@kimmonismusPost on X ·
Whats happening right now is probably way worse than the Hugging Face incident. AI-powered attacks are hitting real organizations while major platforms disclose breaches and critical flaws. - Microsoft reports AI agents targeting hundreds of organizations, reaching privileged cloud access in under three hours in multiple cases. It attributes the ConnectWise compromise to the same group. - CrowdStrike documented four operators running successful AI-agent campaigns. One compromised at least 15 Argentine healthcare organizations. - PHP2Shell: AI helped turn longstanding PHP flaws into working exploits. Cloudflare’s CEO reports millions of exploitation attempts. Their AI involvement is unknown. - Railway disclosed possible access to customer secrets. LiteLLM shipped a backdoored release. Zeabur confirmed another breach and is shutting down. - GitLab patched a maximum-severity flaw affecting 12 years of releases. Node.js patched a serious code-execution vulnerability, with Vercel deploying firewall protections. Feels like a turningpoint.
Open source - TE
TechCrunch@TechCrunchPost on X ·
Microsoft points the blame for ConnectWise's breach at a China-aligned hacker, which relied on AI agents to rapidly hack into thousands of its customers. https://t.co/oTAOqXh3Mg
Open source - DI
Digit@digitindiaPost on X ·
Microsoft says a China-linked hacking group used agentic AI to target 100+ organisations worldwide.🚨 The Storm-0940 campaign reportedly used the ARTEX framework.😳 Here’s what Microsoft says organisations should do:👇 - https://t.co/R1mc7qcuXi #CyberSecurity #Microsoft #AI
Open source - RE
Reuters@ReutersPost on X ·
Chinese-linked hackers compromise ConnectWise, target hundreds in global attack, Microsoft says https://t.co/9WL9Jwa3z4 https://t.co/9WL9Jwa3z4
Open source - BT
Business Today@business_todayPost on X ·
#TechToday | AI-Powered hackers, 2,900 attempts a minute: Microsoft blames China-linked group for AI-assisted ConnectWise cyberattack https://t.co/leDoyxYmlm
Open source - CB
Crypto BriefingArticle ·
Microsoft links Storm-0940 to AI-driven attacks using ARTEX framework The rapid AI-driven attacks highlight the urgent need for enhanced cloud security measures and faster human response to mitigate potential threats. The post Microsoft links Storm-0940 to AI-driven attacks using ARTEX framework appeared first on Crypto Briefing .
Open source - TE
TechmemeArticle ·
Microsoft says China-linked hackers used AI penetration testing tool ARTEX to compromise ConnectWise as part of a campaign targeting hundreds of organizations (AJ Vicens/Reuters) AJ Vicens / Reuters : Microsoft says China-linked hackers used AI penetration testing tool ARTEX to compromise ConnectWise as part of a campaign targeting hundreds of organizations — A Chinese state-aligned hacking group used an AI-driven penetration testing tool to compromise IT services firm ConnectWise as part …
Open source - FI
FIKSCloud@fiks_cloudPost on X ·
An AI agent signed into 2,250+ cloud tenants at ~2,900 attempts a minute. No new exploit. It rode a trusted, over-permissioned OAuth app. Microsoft's read on Storm-0940 + the agentic-AI framework ARTEX 🧵 https://t.co/JsmIBf8poL
Open source - RE
Reuters@ReutersPost on X ·
A Chinese state-aligned hacking group used an AI-driven penetration testing tool to compromise IT services firm ConnectWise as part of a campaign that targeted hundreds organizations globally, Microsoft said https://t.co/hcNiaiaQM5
Open source