

Crypto frontend attacks target multiple DeFi sites with Step Drainer
At least a dozen cryptocurrency project websites were hit by DNS hijacks serving the Step Drainer malicious wallet tool, prompting protocols including Flap, Kintsu, and StonkFun to warn users and restore domains.
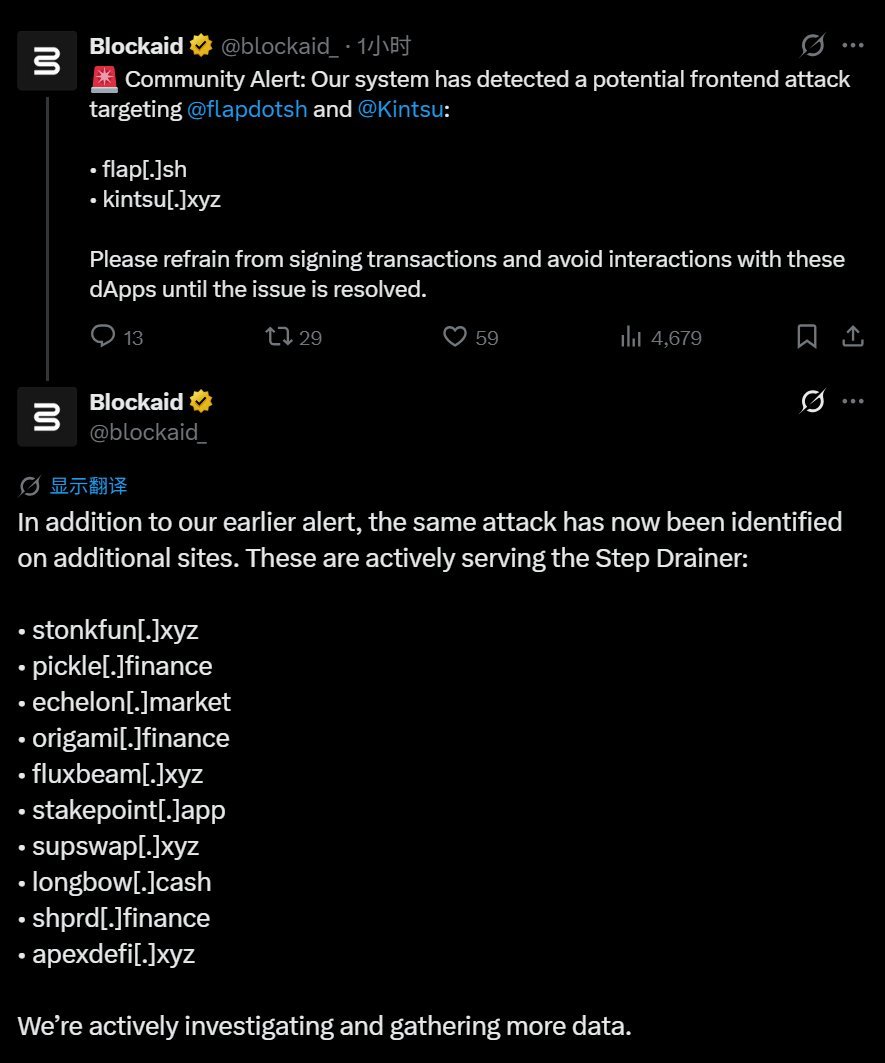
Security firm Blockaid flagged potential frontend attacks early on October 31, initially alerting users to suspicious activity on the websites of token launchpad Flap and protocol Kintsu. Both platforms confirmed DNS hijacks that redirected visitors to unauthorized sites serving the Step Drainer wallet-draining tool, warning users to halt interactions and avoid signing transactions.[1][5][6]
Blockaid subsequently identified 10 additional websites actively serving the drainer, bringing the total number of affected crypto project sites to at least 12. The newly identified domains included stonkfun.xyz, pickle.finance, origami.finance, echelon.market, fluxbeam.xyz, stakepoint.app, supswap.xyz, longbow.cash, shprd.finance, and apexdefi.xyz.[1][5]
Kintsu advised anyone who connected a wallet or signed transactions since approximately 00:00 UTC on October 31 to immediately revoke approvals and move funds. Flap said its underlying smart contracts remained secure and that it implemented a clean redirect to a new domain, with founder Cedric stating that prior visitors to the authentic site were unaffected and pledging that Flap would repay users whose funds were stolen.[1][5]
The Stonk team stated that StonkFun was affected by the wave of domain incidents but confirmed its on-chain operations continued working normally. The team took the website offline and migrated to new infrastructure before restoring it, reporting no known affected users while advising visitors to wait up to an hour before connecting wallets to allow network changes to propagate.[2][3][4]
Key facts
- Security firm Blockaid identified frontend attacks targeting Flap and Kintsu before discovering 10 more domains serving Step Drainer.
- The additional affected sites listed by Blockaid include stonkfun.xyz, pickle.finance, echelon.market, origami.finance, fluxbeam.xyz, stakepoint.app, supswap.xyz, longbow.cash, shprd.finance, and apexdefi.xyz.
- Flap confirmed its flap.sh domain was hijacked and redirected to an unauthorized site, though its smart contracts were unaffected.
- Flap redirected users to a new domain, initiated shutdowns of affected frontends, and pledged to repay users whose funds were stolen.
- Kintsu advised any users who connected wallets or signed transactions after approximately 00:00 UTC on October 31 to revoke approvals and move funds.
- StonkFun stated its on-chain operations remained unaffected, its website was restored on new infrastructure, and no users were known to be impacted.
Sources · 6 sources
- AG
AGTP@AGTPinsightsPost on X ·
Flap just confirmed its https://t.co/m3P35fMnkb website was DNS hijacked and moved users to a new domain. Here's what you need to know. Flap is a BNB Chain token launchpad. Its official domain https://t.co/m3P35fMnkb was hijacked and redirected visitors to a fake, unauthorized site. The team told users not to visit, connect wallets or sign anything. The real URL showed a fake front end, which is what makes DNS hijacks so dangerous. The contracts themselves were fine. The website was the trap. Blockaid flagged it first. Its system detected a potential frontend attack on https://t.co/m3P35fMnkb and https://t.co/Dg8DrqijJn and urged users to stop signing transactions. Kintsu also confirmed a DNS hijack. The alert drew about 24K views. The attack spread. Blockaid says the StepDrainer kit has since hit StonkFun (https://t.co/X6mU631gxG), Pickle Finance, Echelon and others. One count puts it at 13 DeFi sites, another at 12 crypto project websites. Some users asked if the launchpads share infrastructure. Flap's founder warned it may reach other protocols. Flap's response: the team diagnosed the hijack quickly and fixed it with a clean redirect to a new domain. It is shutting down affected frontends. It is still investigating whether its domain service provider was involved, and the root cause is not confirmed. Flap also promised to repay users whose funds were stolen. Key numbers: - Attack began around 00:00 UTC today - 12 to 13 DeFi sites linked to StepDrainer - Blockaid's first alert reached 24K views If you touched Flap or Kintsu since then, revoke your approvals and move your funds.
Open source - CN
crypto.news@cryptodotnewsPost on X ·
JUST IN: Stonk confirms that StonkFun was affected by tonight's attack The domain incident, flagged by Blockaid, targeted multiple DeFi websites with the Step Drainer. Stonk, however, says its onchain operations remain unaffected and urges users not to visit the site or connect wallets until it is confirmed safe.
Open source - SO
SolanaFloor@SolanaFloorPost on X ·
NEW: The Step Drainer attack has been identified on 10 additional websites, including StonkFun, Pickle Finance and Echelon. @LaunchOnSF says its website has been restored after moving to new infrastructure, with on-chain operations unaffected and no known users impacted. https://t.co/mKeDDqqwww
Open source - CB
Crypto Banter@crypto_banterPost on X ·
🚨STONKFUN WEBSITE RESTORED AFTER DOMAIN ATTACK! @LaunchOnSF said the StonkFun site, which was affected by a domain attack on several crypto sites, has been restored after being taken offline and moved to new infrastructure. Everything on-chain continued working normally and the team is not aware of anyone affected. Some networks may take up to an hour to pick up the change, so users are advised to wait before connecting a wallet.
Open source - WB
Wu Blockchain@WuBlockchainPost on X ·
Blockaid: 12 Crypto Project Websites Linked to Frontend Attacks; Flap and Kintsu Confirm DNS Hijacks Security firm Blockaid initially flagged potential frontend attacks targeting Flap and Kintsu. It later identified 10 additional websites serving the Step Drainer wallet-draining tool, including pickle[.]finance, origami[.]finance, and fluxbeam[.]xyz. The investigation is ongoing. Flap and Kintsu have confirmed DNS hijacks affecting their websites, warning users against visiting, connecting wallets, or signing transactions. Flap founder Cedric said users who had previously connected to the legitimate website were unaffected. The risk concerns users who visited the malicious site and connected wallets or signed approvals in the tens of minutes before the announcement. Kintsu advised users who connected wallets or signed anything since approximately 00:00 UTC on October 31 to revoke approvals and move funds. Both projects said they would announce when their websites are safe to use.
Open source - DN
DEGEN NEWS@DegenerateNewsPost on X ·
BREAKING: @flapdotsh SAYS ITS OFFICIAL WEBSITE HAS BEEN HIT BY A "DNS HIJACKING INCIDENT" THE SITE IS "REDIRECTING TO AN UNAUTHORIZED WEBSITE" USERS ARE WARNED NOT TO VISIT IT, CONNECT WALLETS OR SIGN ANY TRANSACTIONS UNTIL FURTHER NOTICE https://t.co/QCXmS8deCz
Open source