

Bitcoin Core patches three vulnerabilities discovered by AI code scanner
Bitcoin Core has published fixes for three security vulnerabilities identified by an automated language-model scanner, bypassing its usual disclosure embargo under newly adopted rules for easily discoverable bugs.
Bitcoin Core published security advisories disclosing three vulnerabilities uncovered through automated scans by Project Loupe, an open-source auditing scanner led by Spiral developer Elias Rohrer and validated by Gregory Sanders. The disclosures accompanied patched maintenance releases across Bitcoin Core versions 29.5, 30.4, 31.2, and 32.1, with no active exploits observed and no network funds placed at risk.[4][3][1]
The most prominent flaw, rated medium severity, allows a malicious peer sending TCP urgent data to bypass incoming queue caps and crash connected nodes running Windows, macOS, or BSD, while Linux systems remain unaffected due to a different socket backend. A second medium flaw enabled connected peers to avoid disconnection by refusing support for BIP 31 nonced pings, steadily inflating message queues by up to 2MB an hour for inbound connections and 5MB an hour for outbound connections.[4][2][5]
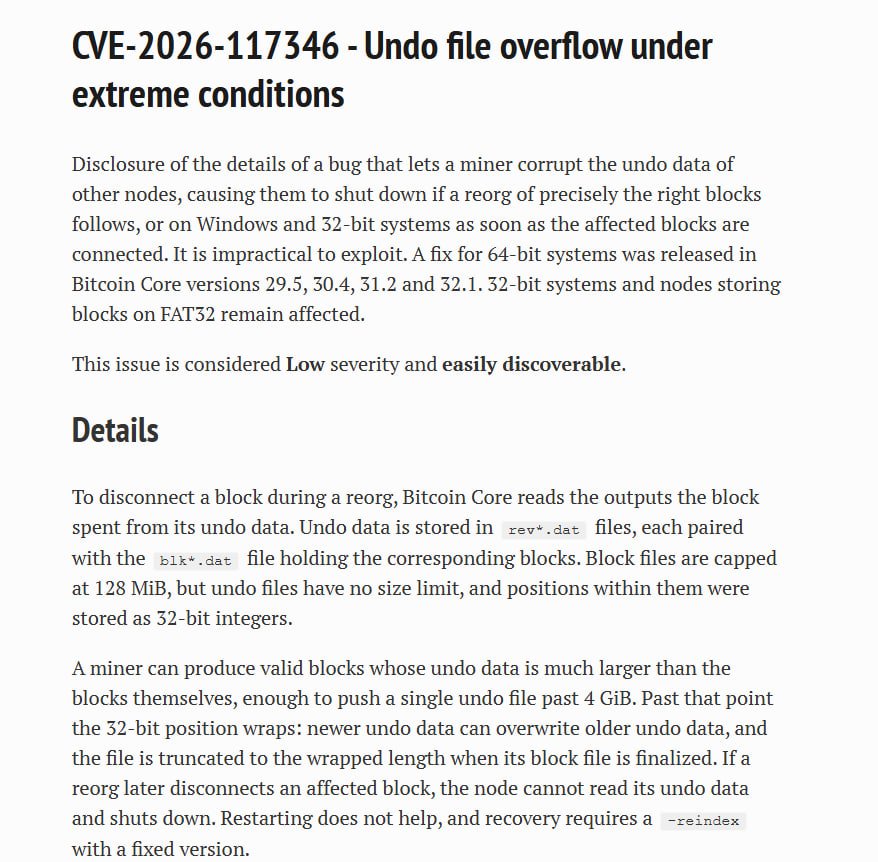
A third issue, cataloged as CVE-2026-117346 and rated low severity, involves undo file overflows in rev*.dat files, where file offsets were stored as 32-bit integers without size limits. An attacker producing valid blocks could theoretically push an undo file past 4 GiB, wrapping the integer position and corrupting undo data required during a blockchain reorganization. While developers deemed exploiting 64-bit systems impractical, 32-bit operating systems and node installations storing block data on FAT32 file systems remain unpatched.[4][7]
Bitcoin Core bypassed its standard one-year embargo period under a policy revision merged on Oct. 22 that fast-tracks advisories for bugs discoverable with minimal effort, such as simple LLM prompts. Following the rollout of the fixes, the Bitcoin Core 29.x series has officially reached its end of life.[4][6][1]
Key facts
- Bitcoin Core published advisories for three vulnerabilities discovered during an automated scan by Project Loupe, led by Spiral's Elias Rohrer and validated by Gregory Sanders.
- Patches addressing the vulnerabilities were shipped in Bitcoin Core versions 29.5, 30.4, 31.2, and 32.1.
- One medium-severity flaw allows malicious peers sending TCP urgent data to crash nodes on Windows, macOS, and BSD, but does not affect Linux nodes.
- A second medium-severity flaw allows peers omitting BIP 31 nonced ping support to resist disconnection, accumulating memory up to 2MB/hour for inbound peers and 5MB/hour for outbound peers.
- Low-severity bug CVE-2026-117346 stems from 32-bit position wrapping in rev*.dat undo files pushed past 4 GiB, which can corrupt undo data and shut down nodes during reorganizations.
- CVE-2026-117346 remains unpatched for 32-bit systems and nodes storing block data on FAT32 file systems.
- Core skipped its typical embargo under an Oct. 22 disclosure policy exception for bugs easily discoverable through methods like simple LLM prompts.
- The Bitcoin Core 29.x version series reached end of life following the October 28 advisory.
Sources · 7 sources
- CR
CryptoSlateArticle ·
Bitcoin developers rush to fix 3 security flaws after AI uncovers them The October 28 advisory identifies four patched releases, but 29.x is now at end of life. Read the full story on CryptoSlate Understand the crypto stories that matter and what to watch next. Get The Catalyst in your inbox
Open source - DE
Decrypt@DecryptMediaPost on X ·
Bitcoin Core discloses 3 vulnerabilities, including a bug that lets a malicious peer crash Windows, macOS and BSD nodes (excluding Linux). https://t.co/Ye6Tt3Qnm7
Open source - CO
CoinMarketCap@CoinMarketCapPost on X ·
HOT TOPIC: AI found 3 bugs that can crash bitcoin:native nodes ⚠️ The headline bug, lets a peer crash nodes on Windows and Mac. Linux is unaffected. Fix shipped in 5 days. No funds at risk, no attacks observed. Is Bitcoin in danger? 👇 https://t.co/4pu4sUyrfy https://t.co/dpbCvBOafL
Open source - UN
UnchainedArticle ·
Bitcoin Core Skips Usual Embargo to Disclose Three Bugs an AI Scan Found Bitcoin Core published three security advisories on Oct. 28, the same day the last of its patched releases went out, skipping its usual embargo. According to the advisories, all three issues turned up in an automated LLM scan by Project Loupe , which Elias Rohrer leads at Spiral. Developer Gregory Sanders validated the findings and brought them to the project’s security team. The advisories do not name the AI model behind the scan. Spiral and Block launched Loupe in May as a free scanner for open-source bitcoin projects, with Bitcoin Core among its first test projects. Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . What the Bugs Do The first bug, rated Medium , affects nodes outside Linux: a peer sending TCP urgent data could slip past the node’s cap on queued incoming data. The advisory said that “a malicious peer can trivially crash any Windows, macOS or BSD node it is connected to.” Linux nodes use a different socket backend and are not affected. Loupe flagged the issue on Oct. 23. A second Medium bug let a malicious peer claim it doesn’t support BIP 31 nonced pings, so the node never dropped it while its outgoing message queue kept growing. Memory could climb up to 2MB an hour per inbound peer and 5MB an hour per outbound one. Loupe reported it on Sept. 15, and developer L0rinc independently flagged it to Sanders on Sept. 21. The third bug , rated Low , lets a miner corrupt the undo files other nodes keep, shutting a node down after a precisely placed reorg, or with no reorg at all on Windows and 32-bit systems. The advisory called an attack on 64-bit systems impractical: it would take several thousand mined blocks carrying nonstandard transactions, “roughly a month of the entire network’s block production.” The patch does not cover 32-bit systems or nodes that keep block data on a FAT32 file system. The advisories don’t say whether any bug was exploited. Why There Was No Embargo Under Bitcoin Core’s disclosure policy , a Medium bug is normally kept private until about a year after its fix first ships. The exception, which Core merged into the policy on Oct. 22, covers “easily discoverable” flaws that “can be discovered with minimal effort, such as through a simple LLM prompt.” Those get a fixed point release for every maintained major version and an advisory as soon as possible. All three advisories carry that label. The fixes are in versions 29.5, 30.4, 31.2 and 32.1 . The 32.1 release notes , dated Oct. 27, say version 32.0 “although tagged, was never fully announced or released.” The notes credit “Anthropic Security” among contributors without saying what it worked on; none of the advisories mentions it. The same notes say Core will disclose three more medium- and high-severity vulnerabilities fixed in version 30.0 in two weeks, on its regular schedule. Related Listen: When Could Quantum Computers or AI Break Bitcoin? An Updated Threat Window The post Bitcoin Core Skips Usual Embargo to Disclose Three Bugs an AI Scan Found appeared first on Unchained .
Open source - CR
CryptoSlate@CryptoSlatePost on X ·
AI-assisted code scanning found three Bitcoin Core flaws, including one that lets a malicious connected peer crash vulnerable Windows, macOS or BSD nodes. @bitcoincoreorg has released fixes; Linux is unaffected by the crash flaw. via @hardeyjumoh https://t.co/TdhpHCEIC8
Open source - LS
Laura Shin@laurashinPost on X ·
Bitcoin Core published three advisories within a day of its last patched release, without the usual embargo. Its policy fast-tracks bugs that "can be discovered with minimal effort, such as through a simple LLM prompt." https://t.co/7QfNd0ru88
Open source - CO
Cointelegraph@CointelegraphPost on X ·
🚨 ALERT: Bitcoin Core discloses a low-severity bug that could let miners corrupt other nodes’ undo data and trigger shutdowns under extreme conditions. https://t.co/66RbLhuzUm
Open source