

Binance exploiter mistakenly burns millions by sending tokens to Newton contract
An attacker behind the recent Binance exploit accidentally transferred around $3.5 million in tokens directly to the Newton Protocol token contract address, permanently locking the funds due to the contract's immutable design.
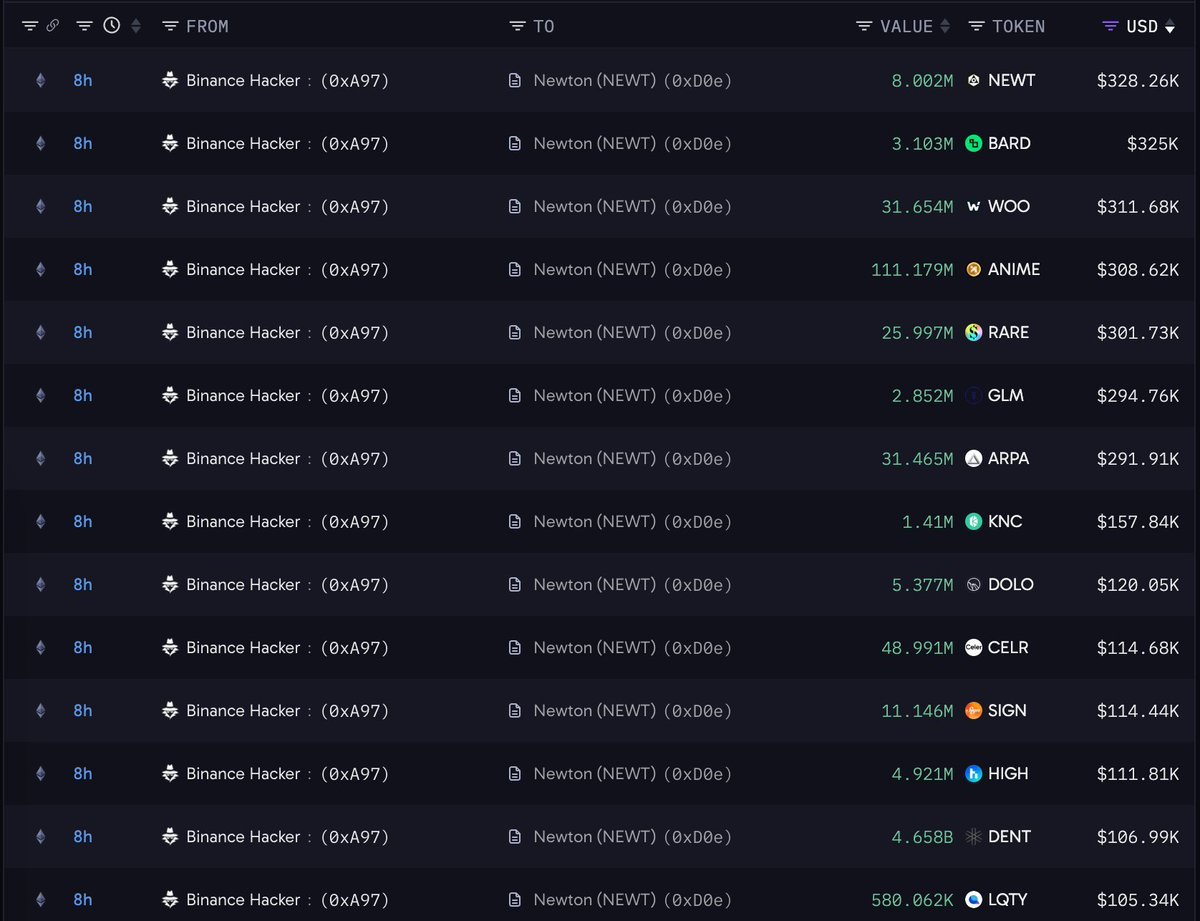
The hacker responsible for the recent Binance exploit has mistakenly sent approximately $3.32 million to $3.5 million in cryptocurrency directly to the Newton (NEWT) token smart contract address, effectively rendering the assets unrecoverable. Lookonchain first flagged the erroneous transfers, which routed millions of tokens from a wallet labeled as the Binance hacker straight into the contract.[2][3]
According to a statement issued by the Newton Foundation, the attacker sent roughly 8.0 million NEWT alongside 17 other tokens, including ANIME, BARD, WOO, RARE, GLM, and ARPA. The foundation confirmed that the token contract itself was not compromised. However, because admin rights were renounced on-chain in 2025 and upgrades are permanently disabled, neither the team nor any third party possesses the keys or capability to retrieve assets sent directly to the contract address.[1][2]
The Newton Foundation stated that the tokens are now permanently out of the attacker's control and cannot enter circulation. The team added that it has shared its findings with Binance and will continue assisting with the investigation. Blockchain intelligence firms Chainalysis and TRM Labs have linked the Binance exploit to North Korea, though no government has officially confirmed the attribution.[1]
Key facts
- The Binance exploiter mistakenly transferred approximately $3.32 million to $3.5 million worth of tokens to the NEWT token contract address.
- The misdirected transfers included around 8 million NEWT alongside 17 other tokens, such as BARD, WOO, ANIME, RARE, GLM, and ARPA.
- The Newton Foundation confirmed the NEWT contract was not breached, but noted the funds are permanently locked because the contract is immutable and has no admin keys.
- Chainalysis and TRM Labs have pointed to North Korea as the actor behind the Binance attack, though government officials have not yet confirmed the claim.
- The Newton Foundation reported that it has shared its analysis with Binance to assist ongoing investigation efforts.
Sources · 3 sources
- DN
DEGEN NEWS@DegenerateNewsPost on X ·
NEW: @binance HACKER "APPARENTLY IN ERROR" SENT ~8M $NEWT AND 17 OTHER TOKENS, WORTH ~$3.5M, STRAIGHT INTO THE $NEWT TOKEN CONTRACT @newtonfndn SAYS THEY'RE NOW "PERMANENTLY LOCKED" @chainalysis AND @trmlabs POINT TO NORTH KOREA, BUT NO GOVERNMENT HAS CONFIRMED IT YET https://t.co/tvyyjRcvca
Open source - LO
Lookonchain@lookonchainPost on X ·
The Binance hacker sent ~$3.32M worth of altcoins to the $NEWT token contract address by mistake. The funds are now unrecoverable. https://t.co/dsvDnXRn1b https://t.co/nzfuvnqgvZ
Open source - CB
Crypto Banter@crypto_banterPost on X ·
🚨BINANCE HACKER ACCIDENTALLY SENDS ~$3.5M IN TOKENS TO NEWT CONTRACT ADDRESS, FUNDS NOW STUCK! @binance hacker sent roughly $3.32-3.5 million worth of tokens, including about 8 million $NEWT plus other altcoins, directly to the NEWT token contract address by mistake, per @lookonchain. $NEWT is the native token of Newton Protocol, an on-chain automation project. The Newton Foundation confirmed the contract itself was not compromised. Because it is immutable, has no admin keys, and cannot be upgraded, no one can recover tokens sent to the contract address. The funds are permanently locked.
Open source