Ledger details cellular spy implants in reseller wallets as stolen funds top $100 million
Hardware wallet maker Ledger revealed that tampered signers sold through Southeast Asian reseller CryptoBilis contained covert cellular implants that intercepted recovery phrases, while third-party researchers estimate total losses have reached $102 million.
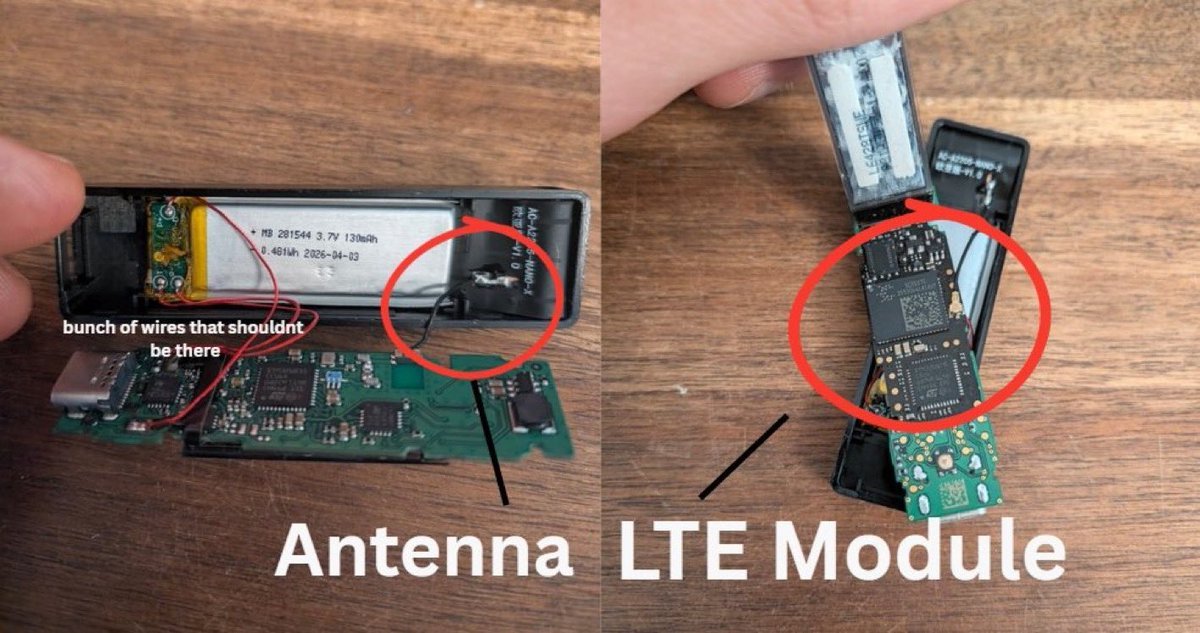
Ledger's Donjon security team disclosed that modified hardware wallets sold through reseller CryptoBilis contained covert physical implants designed to steal wallet recovery phrases during setup. According to the company, an unauthorized microcontroller embedded in the device casing read 24-word phrases directly off the screen and transmitted them over cellular LTE networks using a provisioned eSIM. Ledger stressed that the add-on component functioned without altering its Secure Element chip, operating system, or transaction signing processes.[9][4][8][2]
The scale of the attack has escalated according to on-chain analysts. Blockchain data firm Bitquery counted $102.0 million drained across 324 wallets on six blockchains, noting that stablecoin issuer Tether has frozen $10.0 million across 20 addresses linked to the incident. Ledger has not verified an official loss total or confirmed user tally, but stated that every confirmed theft connected to the October 9 incident traces directly to devices sold by Malaysia-based CryptoBilis.[1][3][7][9]
Following the disclosures, CryptoBilis halted sales of hardware wallets, and competitors Trezor and OneKey cut ties with the reseller. Meanwhile, users on social media reported tampered devices purchased through other authorized distributors, including German retailer MediaMarkt and Philippine reseller LazMall. Former Mt. Gox CEO Mark Karpeles noted that some implants could record seed phrases while evading Ledger's Genuine Check security tool. Ledger CEO Pascal Gauthier said internal systems remain uncompromised and an investigation is underway to determine where supply chain tampering took place.[5][6][10][9]
Key facts
- Ledger confirmed that tampered wallets sold by reseller CryptoBilis contained an unauthorized microcontroller and eSIM that transmitted 24-word recovery phrases over LTE.
- Blockchain data firm Bitquery tracked $102.0 million stolen across 324 wallets on six blockchains connected to the exploit.
- Tether has frozen $10.0 million in USDT spread across 20 addresses linked to the wallet drains.
- Ledger stated that the hardware implants left the Secure Element and its operating system unmodified.
- Hardware wallet makers Trezor and OneKey severed ties with reseller CryptoBilis after the tampering came to light.
- Former Mt. Gox CEO Mark Karpeles stated that the spy implants could capture seed phrases while evading Ledger's Genuine Check protocol.
Sources · 8 sources
- UN
UnchainedArticle ·
After the Ledger Reseller Hack, Austin Campbell Says Self-Custody Users Should Be ‘Over-Solving for Simplicity’ Austin Campbell , founder of Zero Knowledge Group, said the wallet drains tied to Ledger devices sold through the reseller CryptoBilis pointed to “a big misunderstanding of information security in this space.” Campbell said on the show, Bits + Bips, recorded Oct. 12, that many tools people use to guard their own keys “rely upon a bunch of things like vendors you cannot really do diligence, or devices that you can’t easily take apart and understand, and this is where people have got themselves into trouble.” He offered a hypothetical: a hot wallet whose private key was written down, stored in a fully encrypted password manager and never used to send a transaction. He said “nothing’s been stolen” from a wallet set up that way. Campbell added that he did not agree with the popular view that a wallet is unsafe unless it sits in cold storage. “When you’re an individual, you have limited time and limited ability to verify,” he said, adding that individuals “should actually be over-solving for simplicity” if they want to hold their own crypto. Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . What Ledger Has Said Ledger Support confirmed on Oct. 10 that one impacted user’s device carried an unauthorized hardware implant . In an Oct. 11 update , the company wrote that “the volume of impacted devices is limited” and that every confirmed case so far involved devices sold through CryptoBilis, its reseller in Southeast Asia. Ledger has not given a loss total. Blockchain data firm Bitquery counted $102.0 million taken from 324 wallets on six chains as of Oct. 12, up from an earlier $93.2 million count that Unchained cited in its story on Ledger’s update. Bitquery also said Tether has frozen $10.0 million linked to the theft. Perkins Sees a Role for Intermediaries Co-host Chris Perkins , head of Franklin Crypto, drew a different lesson. “There’s no choice. You gotta use an intermediary,” he said, adding that holding personal wealth in decentralized finance is hard for anyone who is vulnerable. “Intermediaries should not be necessary, but they may be wanted,” Perkins said. He described crypto as being at “max security vulnerability” right now and also said, “You can’t eliminate trust, sadly.” Both hosts called for a broader response to hacks. Campbell said “right now the incentives for hacking are all one way,” and warned that “you end up in a world where the bad actors have maximum power” when a system is fully permissionless and traditional laws are hard to enforce. Related Listen: Bitcoin Custody Has 5 Levels. Where Should Your Keys Actually Live? The post After the Ledger Reseller Hack, Austin Campbell Says Self-Custody Users Should Be ‘Over-Solving for Simplicity’ appeared first on Unchained .
Open source - DE
DecryptArticle ·
Ledger Finds LTE Implant That Stole Recovery Phrases in Suspected $86M Drain Ledger says the hidden chip reads the 24-word phrase off the screen during setup, leaving the Secure Element and its software untouched.
Open source - UN
UnchainedArticle ·
Ledger Says All Confirmed Cases Trace to Reseller CryptoBilis, Gives No Loss Total Ledger said on Oct. 11 that “the volume of impacted devices is limited,” and that every confirmed case in the Oct. 9 wallet drains traces back to one seller. “To date, all confirmed cases related to the disclosed draining incident of Oct 9th, 2026, involve devices sold through the Southeast Asia reseller CryptoBilis,” the hardware wallet maker wrote, adding, “Our systems and direct sales channels remain unaffected.” The 72-hour update did not include a loss figure , a count of affected devices, or an explanation of how the devices were tampered with. Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . What Ledger Told Buyers A day earlier, the Ledger Support account said in a post on X that “one of the impacted users’ devices contained an unauthorized hardware implant.” It added that CryptoBilis had stopped selling hardware wallets until the investigation ends. Ledger told CryptoBilis customers not to set up unused devices and, if they already had, to move to a new recovery phrase on a device from Ledger. It said it is working with authorities, reviewing controls on its authorized resellers, and reminding them “never to restock returned products.” How Much Was Taken Without a number from Ledger, the totals come from onchain trackers, and they do not agree. Blockchain data firm Bitquery tallies $93.2 million across six blockchains, pulled from 315 wallets and mostly held as USDT on TRON. Security research site YFarmX puts the figure at $103.4 million from 530 addresses on seven blockchains, after adding nine more drained TRON wallets in an Oct. 12 update. Unchained first reported the drains on Oct. 9, when early tallies were built from a handful of public addresses. Where the Money Went Per Bitquery, Tether blocked 37 addresses linked to the theft, leaving $10 million in USDT frozen across 20 of them. The blockchain data firm said it traced 2,990 ETH that the thief pushed through Tornado Cash and then Zcash to seven wallets, five of which held 5.35 million USDC on Oct. 11 and were emptied, ahead of any freeze. Bitquery put the amount it could still follow onchain at about $86 million on Oct. 11. “The record points to one actor who held the keys to every one of those wallets,” Bitquery wrote in its investigation , while noting that “the chain cannot show where the keys leaked from.” Related Listen: Bitcoin Custody Has 5 Levels. Where Should Your Keys Actually Live? The post Ledger Says All Confirmed Cases Trace to Reseller CryptoBilis, Gives No Loss Total appeared first on Unchained .
Open source - TW
The Wolf Of All Streets@scottmelkerPost on X ·
UPDATE: LEDGER SAYS COVERT IMPLANT IN CRYPTOBILIS-SOLD DEVICES READ 24-WORD RECOVERY PHRASES FROM SCREENS AND TRANSMITTED THEM OVER LTE VIA MICROCONTROLLER AND ESIM
Open source - CT
Coin TelegraphArticle ·
Ledger details LTE-enabled spy implants in wallets sold by CryptoBilis Ledger detailed how LTE-enabled implants exposed wallet recovery phrases as CryptoBilis halted sales and Trezor and OneKey cut ties with the reseller.
Open source - PR
ProtosArticle ·
Ledger spyware scare spreads beyond Southeast Asia More examples of Ledger wallets being tampered with and fitted with physical spyware have allegedly been identified across Asia, Europe, and South America. Ledger users who bought hardware wallets from Malaysia-based reseller CryptoBilis were drained of over $86 million last week. Former Mt. Gox CEO Mark Karpelès discovered that spyware implanted in some Ledger devices was being used to read their screen output. It could record any seed phrase while remaining undetected by Ledger’s Genuine Check security protocol. Ledger confirmed yesterday that the incident on October 9 affected a “limited” number of devices sold by CryptoBilis. “We are reminding our authorized resellers and distributors to source products only through authorized channels and never to restock returned products,” it said. More Ledger wallets flagged with spyware Self-proclaimed semi-professional airdrop farmer “@0xJohannes_” claimed to have unpacked a Ledger device with a spy implant that was bought directly from Ledger’s official German reseller MediaMarkt. The device did not appear to redirect any funds to an exploiter, with the X user noting, “Either the device didn’t work or they were waiting for a more widespread usage of the comprised devices.” They also claimed that “there are reported cases in Asia, South America, and now Europe as well.” PSA the ledger incident isn't limited to Asia This is a device purchased in store from an official reseller in Europe (a legitimate device doesn't have any of these cables as can be seen in picture 2) This even seems to be an old version of the 'spy implant' even though the… pic.twitter.com/bLWrN9aooK — Johannes (4, 4) (@0xJohannes_) October 11, 2026 Read more: Ledger says Southeast Asia reseller linked to $86M draining Another X user, “@Us_Chan007,” shared pictures of the interior of a Ledger wallet they bought from official Philippine reseller LazMall. Karpelès noted this wallet was fitted with an earlier style of spyware in the form of a “manual coil antenna.” He also helped identify spyware implanted in one of Ledger’s Stax models shared by X user @wentrre, who’d also bought from CryptoBilis. Very much a problem! Move your assets as soon as possible from any seed that touched this device — Mark Karpelès (@MagicalTux) October 11, 2026 Read more: Ledger sued for $500M over its many data breaches Despite these examples, there are also dozens of users dismantling their Ledger devices out of caution only to be told by Karpelès that they’re “clean.” Former CryptoBilis exec says firm is under new management At one point this weekend, attention turned to CryptoBilis’ former CEO, Arravind Prabu, who revealed in an exchange on X that the firm was acquired earlier this year, and that he’s stepped down from all operations. When quizzed about CryptoBilis’ recent Lamborghini and pizza post, he claims that the account is under new management and that former staff signed a confidentiality clause that meant they couldn’t reveal the company was under new ownership. Got a tip? Send us an email securely via Protos Leaks . For more informed news and investigations, follow us on X , Bluesky , and Google News , or subscribe to our YouTube channel. The post Ledger spyware scare spreads beyond Southeast Asia appeared first on Protos .
Open source - AI
Analytics Insight@analyticsinmePost on X ·
𝐋𝐞𝐝𝐠𝐞𝐫 𝐂𝐨𝐧𝐟𝐢𝐫𝐦𝐬 𝐇𝐚𝐫𝐝𝐰𝐚𝐫𝐞 𝐈𝐦𝐩𝐥𝐚𝐧𝐭 𝐢𝐧 𝐂𝐫𝐲𝐩𝐭𝐨 𝐖𝐚𝐥𝐥𝐞𝐭 𝐋𝐢𝐧𝐤𝐞𝐝 𝐭𝐨 𝐔𝐒𝐃 𝟏𝟎𝟐 𝐌𝐢𝐥𝐥𝐢𝐨𝐧 𝐓𝐡𝐞𝐟𝐭 🚨 Ledger confirms a hidden hardware implant in a crypto wallet sold by CryptoBilis as researchers estimate losses of USD 102 million across 324 wallets. The company says its internal systems remain secure and urges affected users to replace their devices and recovery phrases. 🔐⚠️ #Ledger #CryptoBilis #CryptoHack #CryptoSecurity #HardwareWallet #analyticsinsight #analyticsinsightmagazine Read More 👇 https://t.co/BhInyCiO0A
Open source - BS
BSCN@BSCNewsPost on X ·
Ledger Uncovers Hidden Spy Implants in Hardware Wallets Ledger (@Ledger) says modified wallets sold by reseller CryptoBilis secretly captured users’ recovery phrases. The malware decoded the 24-word phrase shown at the time of setting up the device and sent it over LTE through the SIM card installed in the device. Ledger says that neither the security chip nor the signing process was affected. Losses could amount to more than $100 million, but there is no confirmation from Ledger. Images: Ledger and Johannes (4, 4) X platform
Open source - UN
UnchainedArticle ·
Ledger Says Unauthorized Component in CryptoBilis Wallets Leaked Recovery Phrases Over Cellular Setting up a Ledger signer bought from Southeast Asian reseller CryptoBilis was enough to expose a buyer’s 24-word recovery phrase , according to Ledger’s Donjon researchers, who traced the leak to an unauthorized, separate component installed inside the device. In an Oct. 13 update , Ledger said the implant, which its Donjon team is analyzing, “sits inside the enclosure and reads the data shown on the screen.” Once the device shows the recovery phrase during setup, Ledger said, “its microcontroller decodes the words and transmits them over LTE using a provisioned eSIM.” Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . A Separate Chip Ledger described the implant as an added part rather than a change to its own hardware or software. “It does not modify the Secure Element or the Ledger operating system, and it does not alter transactions or signatures,” the company wrote. The Secure Element is the chip that stores a wallet’s private keys. Every confirmed fund loss tied to the incident Ledger disclosed on Oct. 9 involves a device sold through CryptoBilis, according to the company. It added: “We have not verified a drain linked to a signer bought elsewhere.” Ledger also said it is “reviewing reports of implants in other signers and locations.” Still Counting Cases Ledger said it has not confirmed the number of affected users or the total amount lost, and that “figures circulating online come from third parties and Ledger has not fully verified them.” Ledger asked users whose funds were drained to contact Ledger Support so their cases can be counted. Ledger first asked CryptoBilis to pause sales on Oct. 9, later confirming that one affected user’s device contained “an unauthorized hardware implant.” CryptoBilis has since stopped selling Ledger devices, Ledger said. CEO Pascal Gauthier wrote that “the investigation is ongoing to determine who tampered with these signers or where in the distribution chain it happened.” He said the company has “no indication that Ledger’s infrastructure, systems or services were compromised” and is reviewing the controls that cover both its direct sales and its resellers. “Physical supply chain tampering is a risk for the whole industry,” Gauthier wrote. Guidance for Buyers Ledger told CryptoBilis buyers who have not yet set up a device to leave it untouched and contact support, and those who already have to move their assets to a new device with a fresh recovery phrase. Owners of a possibly tampered device should talk to Ledger Support or police before shipping it anywhere, the company said. For people who bought elsewhere, Ledger published a guide to opening a device and inspecting its interior, noting that doing so can damage the hardware. The Donjon team will examine devices it receives and share more findings as the investigation continues, Ledger said. Related Listen: Bits + Bips: Is Any Cold Wallet Safe? Inside the Coldcard Hack’s Wave Three The post Ledger Says Unauthorized Component in CryptoBilis Wallets Leaked Recovery Phrases Over Cellular appeared first on Unchained .
Open source - CO
CoindeskArticle ·
Ledger says 'spy' chip inside CryptoBilis Ledger devices transmitted wallet keys over mobile network Ledger announces MediaMarket Saturn also stopped selling devices after a customer found a corrupted signer in Germany. It also it is investigating who tampered with the devices.
Open source