Lighter resumes withdrawals after returning 5 million USDC to exploited trader
Perpetual futures exchange Lighter has restored deposits and withdrawals following a security incident that saw an attacker derive trader API keys through nonce reuse in third-party signing code.
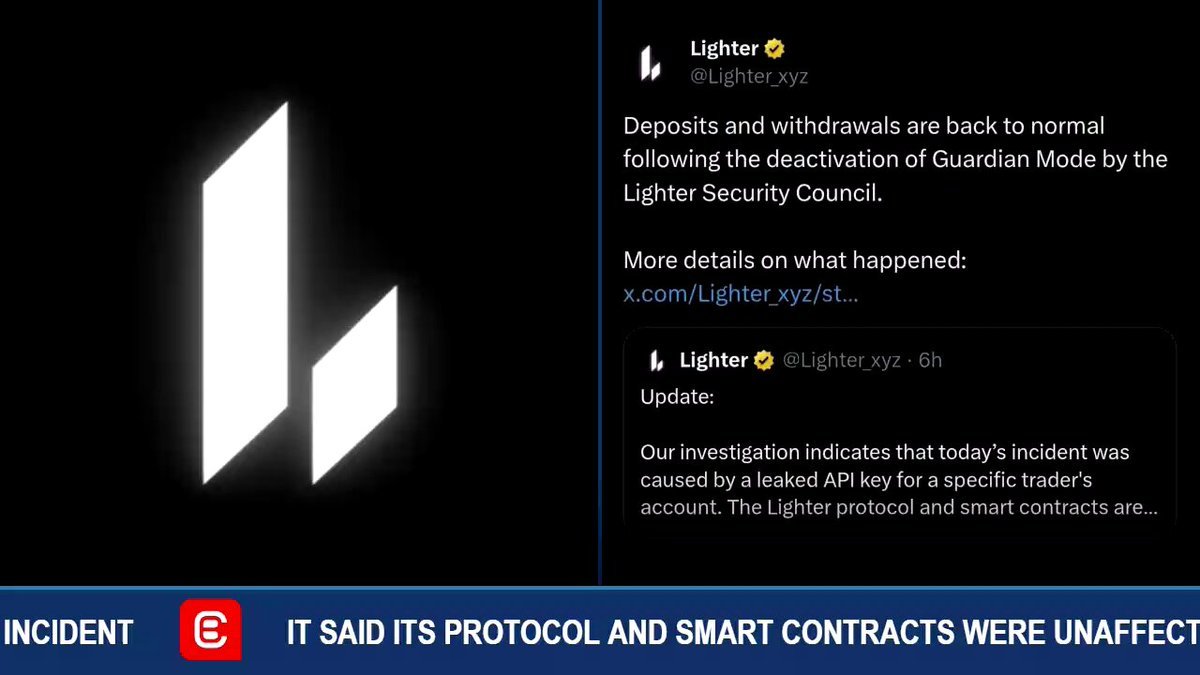
Perpetual futures exchange Lighter has reopened deposits and withdrawals after its Security Council deactivated Guardian Mode, concluding an emergency intervention that returned approximately 5 million USDC to an affected trader.[1][3]
According to Lighter's post-mortem, the breach occurred on the morning of November 16 after an attacker derived private API keys by exploiting nonce reuse in unofficial, third-party signing code used by the trader. Every transaction on the exchange requires an API signature with a fresh random number; because signatures were public, repeating nonces enabled the attacker to compute the underlying private keys. Lighter affirmed that its core protocol, smart contracts, infrastructure, and official software development kits were unaffected.[1][3]
Once inside the account, the attacker launched a public pool from the victim's profile, transferred the trader's funds into the vault, and redeemed the assets through a separate account under the attacker's control. The unusual transfer activity triggered Lighter's Guardian safeguard, pausing platform withdrawals and allowing the Security Council to intercept an additional withdrawal attempt and return 5 million USDC to the victim.[1][2][3]
While Lighter has not published an official total loss figure, pseudonymous researcher 0xTria estimated that roughly $15.5 million was extracted across two market-maker accounts, and on-chain trackers reported around $10.4 million in USDC had been converted to ether and moved to Hyperliquid. Lighter has since mandated wallet signatures for public pool transfers, stopped broadcasting API key signatures publicly, and announced plans for IP allowlisting, configurable per-key limits, and active monitoring for nonce reuse.[1][2][3]
Key facts
- Lighter reopened deposits and withdrawals after its Security Council deactivated Guardian Mode.
- Approximately 5 million USDC was recovered and returned to an affected trader.
- The exploit was traced to nonce reuse in unofficial signing software, which allowed the attacker to derive API private keys from public signatures.
- Lighter confirmed its protocol, smart contracts, infrastructure, and official SDKs were not compromised.
- The attacker extracted funds by opening a public pool on the victim's account and redeeming shares through an attacker-controlled account.
- Lighter added wallet signature requirements for pool transfers and ceased making API key signatures publicly visible.
- Researcher 0xTria estimated total losses at approximately $15.5 million across two accounts, though Lighter has not confirmed a total loss figure.
Sources · 3 sources
- UN
UnchainedArticle ·
Lighter Reopens Withdrawals, Hands 5 Million USDC Back to Drained Trader About 5 million USDC is back with a trader whose Lighter accounts were drained Monday morning, and the perpetual futures exchange has let withdrawals flow again. Its post-mortem on X says the trader’s signing setup, which skipped Lighter’s official software development kits (SDKs), gave away the trader’s application programming interface (API) keys, the credentials that sign the account’s transactions. Lighter said in a separate post on X that “deposits and withdrawals are back to normal following the deactivation of Guardian Mode by the Lighter Security Council.” Queued withdrawals are going through, the post-mortem said. Earlier Monday, Lighter had pinned the drain on a leaked API key and said its contracts were not hit. Lighter said its Guardian, a recently launched smart contract safeguard, caught the anomaly and froze withdrawals, letting the Security Council return the funds. Lighter founder and CEO Vladimir Novakovski who discussed Lighter’s Robinhood perps deal with Unchained in July, added that the exchange’s escape hatch “provides a safety net in the event of a protocol-wide attack (which this was not, thankfully).” Get Unchained’s crypto news in your inbox with the free Unchained Daily newsletter . How the Keys Leaked Every transaction on Lighter, from orders to fund transfers, is signed with an API key. Each signature should carry a fresh random number, a nonce . Lighter said the trader’s code, built outside its official SDKs, repeated nonces. Signatures are public, so two sharing a nonce let the attacker work out the key itself. A key can’t withdraw to anyone else’s wallet, but Lighter lets it fund its own account’s sub-accounts, and any public pool that account opens, a vault where depositors buy shares and an operator trades for them, falls in that group. The attacker opened a pool from the victim’s account, used a separate account it controlled to buy pool shares, moved the victim’s balance in, then cashed out. Why It Matters for Bot Traders The flaw sat in the trader’s own software, so the same risk applies to any account whose own signing code mishandles nonces; Lighter noted that nonce reuse breaks Bitcoin and Ethereum signatures too. Lighter now demands a wallet signature before funds go into a public pool and has stopped exposing API key signatures. IP allowlists, per-key limits and monitoring that voids any key caught reusing a nonce are next. It told traders unsure of their code to rotate keys and use an official SDK. Pseudonymous researcher 0xTria estimated about $15.5 million was taken from two market-maker accounts, $10.39 million and $5.09 million, figures Lighter, which has not given a total loss, has not confirmed. Related Listen: Ledger Wallets Were Drained of $100 Million. Is Self-Custody Still Safe? The post Lighter Reopens Withdrawals, Hands 5 Million USDC Back to Drained Trader appeared first on Unchained .
Open source - CB
Crypto Banter@crypto_banterPost on X ·
🚨LIGHTER RESTORES DEPOSITS AND WITHDRAWALS AFTER LEAKED API KEY INCIDENT! @Lighter_xyz announced that deposits and withdrawals are back to normal after its Security Council deactivated Guardian Mode. Earlier today the perpetuals exchange traced the incident to a leaked API key on one trader’s account. It said its protocol and smart contracts were unaffected, paused withdrawals as a precaution, and enabled Guardian Mode while prioritizing recovery of funds from an additional withdrawal attempt by the attacker. On-chain trackers reported roughly $10.4 million in USDC withdrawn from the platform (with some higher unconfirmed estimates), with funds moved into ETH and then to Hyperliquid.
Open source - WB
Wu Blockchain@WuBlockchainPost on X ·
Lighter Security Incident Update: Approximately 5M USDC Returned to Affected Trader, Withdrawals Resumed Lighter said in its November 16 security incident report that an attacker exploited nonce reuse in unofficial signing code used by certain trading accounts to derive API private keys from public signatures. The attacker then created a public pool through a compromised account, transferred funds into the pool, and extracted assets by redeeming pool shares through an attacker-controlled account. Lighter confirmed that its protocol, smart contracts, infrastructure, and official SDKs were unaffected. The incident triggered its smart contract-based Guardian mechanism, temporarily pausing withdrawals and allowing the Security Council to return approximately 5 million USDC to the affected trader. Withdrawals have since resumed, with pending requests being processed. Lighter has implemented wallet signature requirements for public pool transfers and made API key signatures non-public. It also plans to introduce IP allowlists, per-key permissions and limits, and proactively monitor and revoke API keys at risk from nonce reuse.
Open source