Hackers hijack Ethersphere's bee-js package and Swarm Desktop to distribute malware
Attackers compromised maintainer accounts to distribute cryptocurrency wallet-stealing malware and backdoors across Windows, macOS, and Linux through Ethersphere's bee-js npm package and Swarm Desktop app.
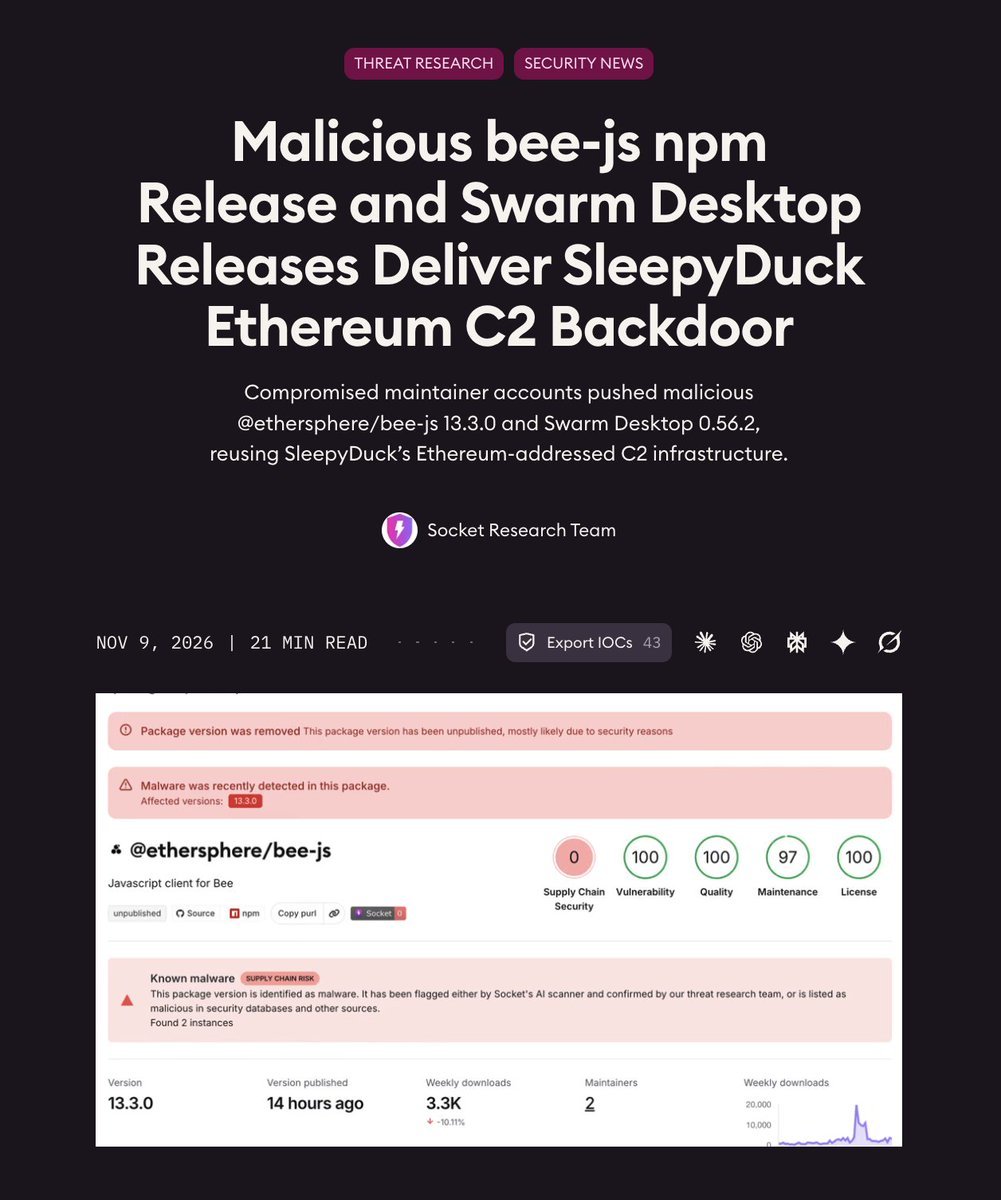
Attackers hijacked Ethersphere's bee-js npm package and the Swarm Desktop application to distribute cryptocurrency wallet-stealing malware and persistent backdoors across Windows, macOS, and Linux systems, according to reports from SolanaFloor and Solid Intel.[1][2][3]
Research documented by the Socket Research Team and shared by SolanaFloor indicated that compromised maintainer accounts published malicious releases of @ethersphere/bee-js version 13.3.0 and Swarm Desktop version 0.56.2. The malicious payloads reused Ethereum-addressed command-and-control infrastructure linked to SleepyDuck. Package registry data showed the compromised bee-js release had around 3.3K weekly downloads before it was flagged as known malware and unpublished.[1]
Both compromised releases have since been removed. Users who downloaded the affected versions are advised to eliminate any persistent backdoors installed on their systems and immediately replace compromised cryptocurrency wallet keys.[1]
Key facts
- Hackers hijacked Ethersphere's bee-js npm package and the Swarm Desktop application to push wallet-stealing malware.
- The malware and backdoors affected Windows, macOS, and Linux operating systems.
- Compromised maintainer accounts pushed malicious releases @ethersphere/bee-js 13.3.0 and Swarm Desktop 0.56.2, according to the Socket Research Team.
- The compromised software reused SleepyDuck's Ethereum-addressed command-and-control infrastructure.
- Both malicious releases were removed, and affected users were urged to remove persistent backdoors and replace compromised wallet keys.
- The bee-js package had approximately 3.3K weekly downloads and was unpublished after being flagged as known malware.
Sources · 3 sources
- SO
SolanaFloor@SolanaFloorPost on X ·
NEW: Hackers hijacked Ethersphere’s bee-js npm package and Swarm Desktop app to distribute crypto wallet-stealing malware and backdoors on Windows, macOS, and Linux. Both malicious releases were removed. Affected users must also remove persistent backdoors and replace compromised wallet keys.
Open source - CB
Crypto BriefingArticle ·
Hackers hijack Ethersphere’s bee-js package and Swarm Desktop app to push wallet-stealing malware The incident underscores the critical need for robust security measures in software supply chains, as trust in official channels is exploited. The post Hackers hijack Ethersphere’s bee-js package and Swarm Desktop app to push wallet-stealing malware appeared first on Crypto Briefing .
Open source - SI
Solid Intel 📡@solidintel_xPost on X ·
INTEL: Hackers hijack Ethersphere's bee-js npm package and Swarm Desktop app to push crypto wallet-stealing malware
Open source